All the articles with the tag "excessive-agency".
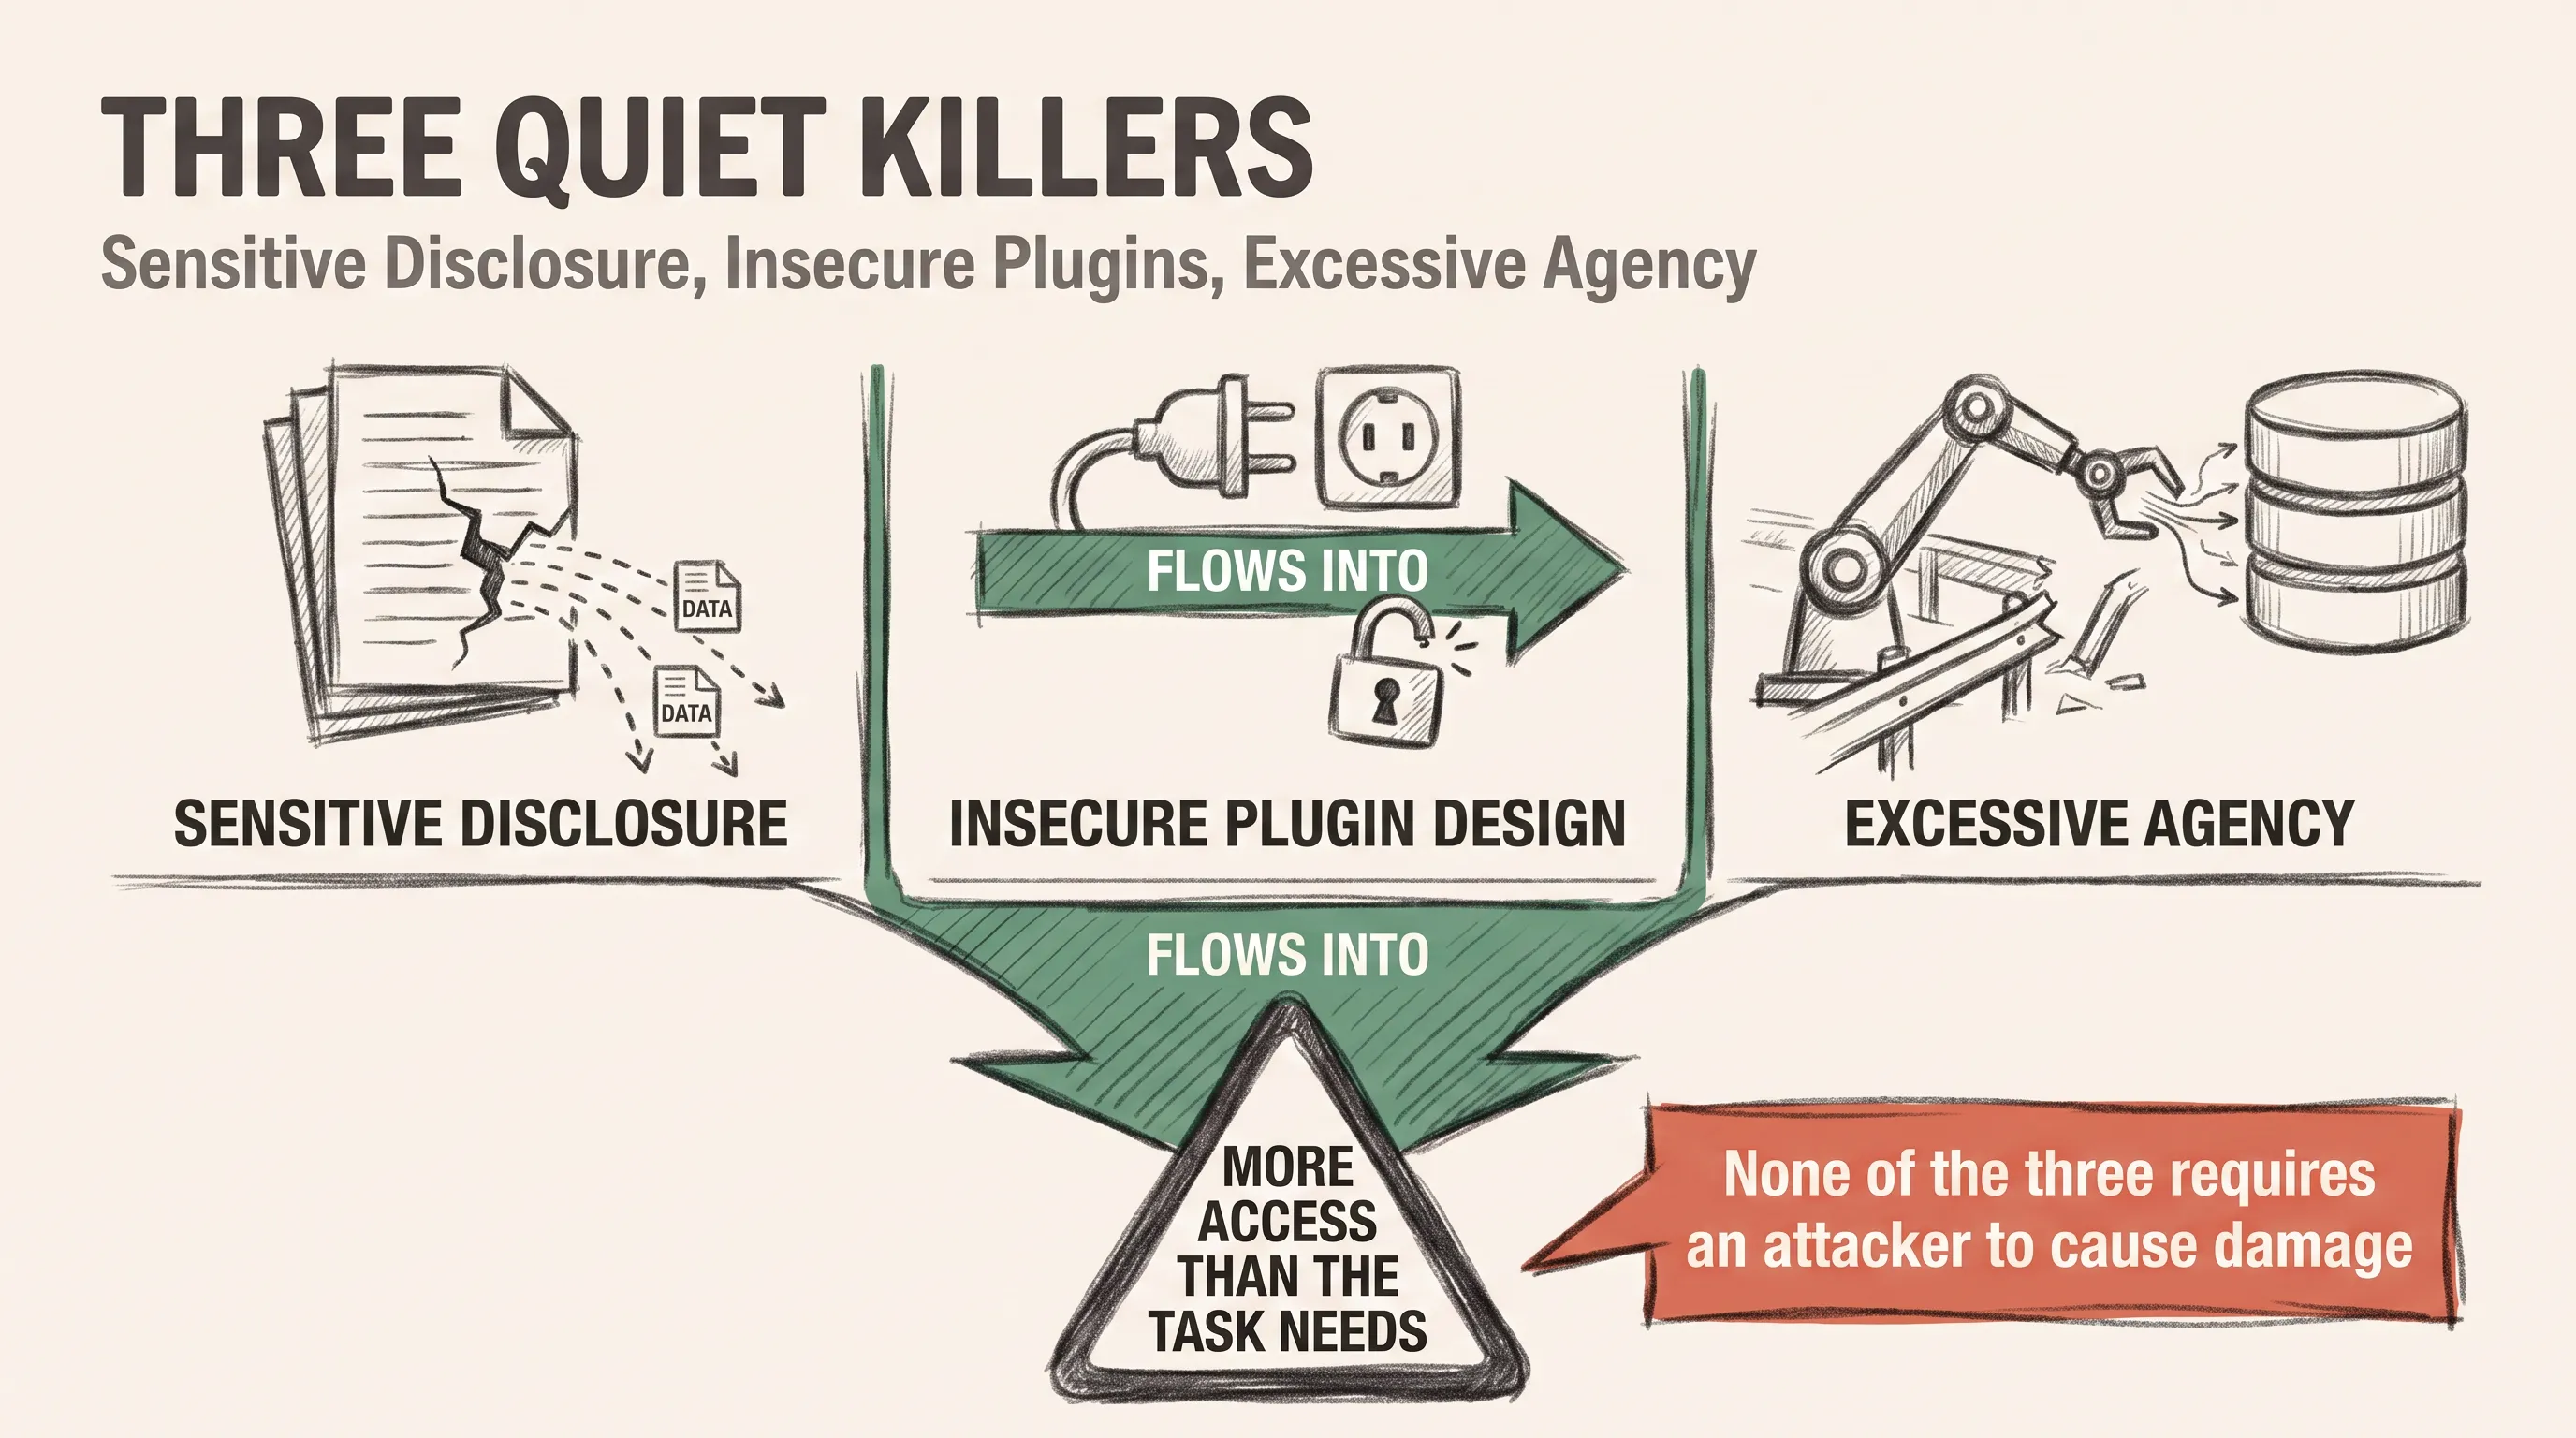
Three under-discussed OWASP LLM risks: sensitive data leakage, insecure plugin design, and excessive agent autonomy, with mitigations for each.