Tag: owasp
All the articles with the tag "owasp".
-
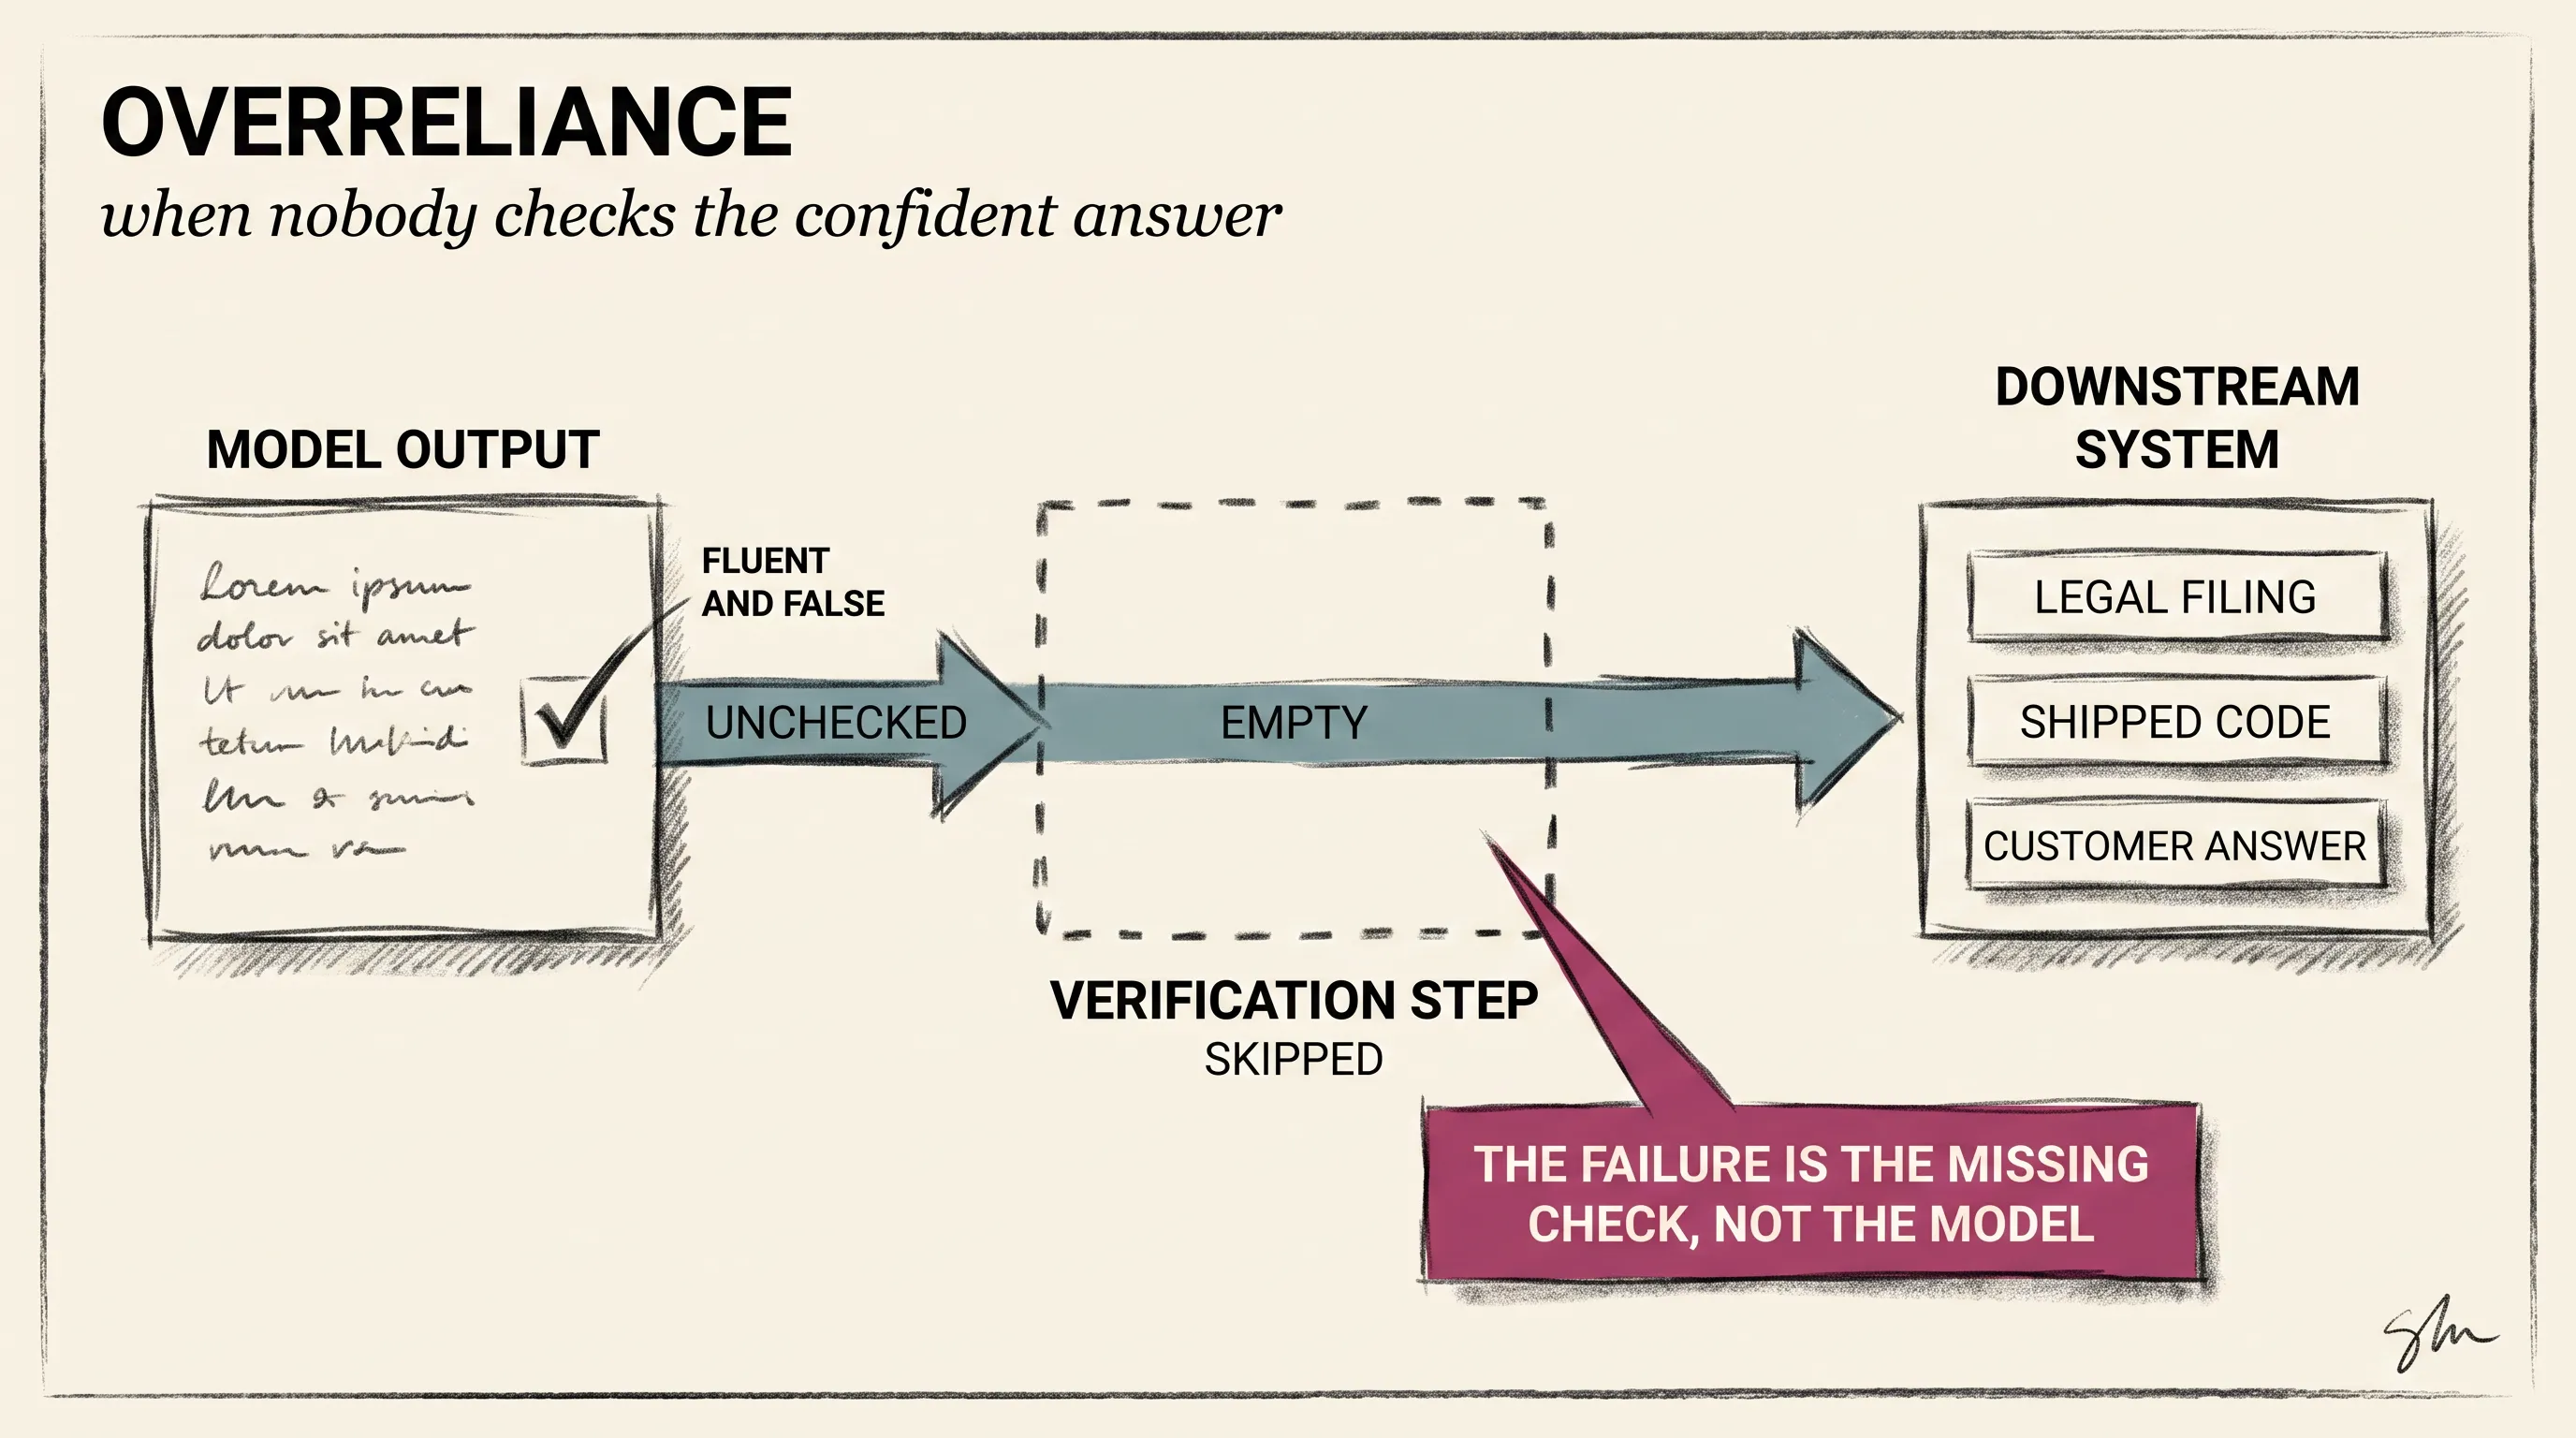 llm-security9 min read
Overreliance and the Hallucination Problem
What LLM hallucinations are, why they happen, documented overreliance failures in law and code, and the mitigations that actually reduce the damage.
-
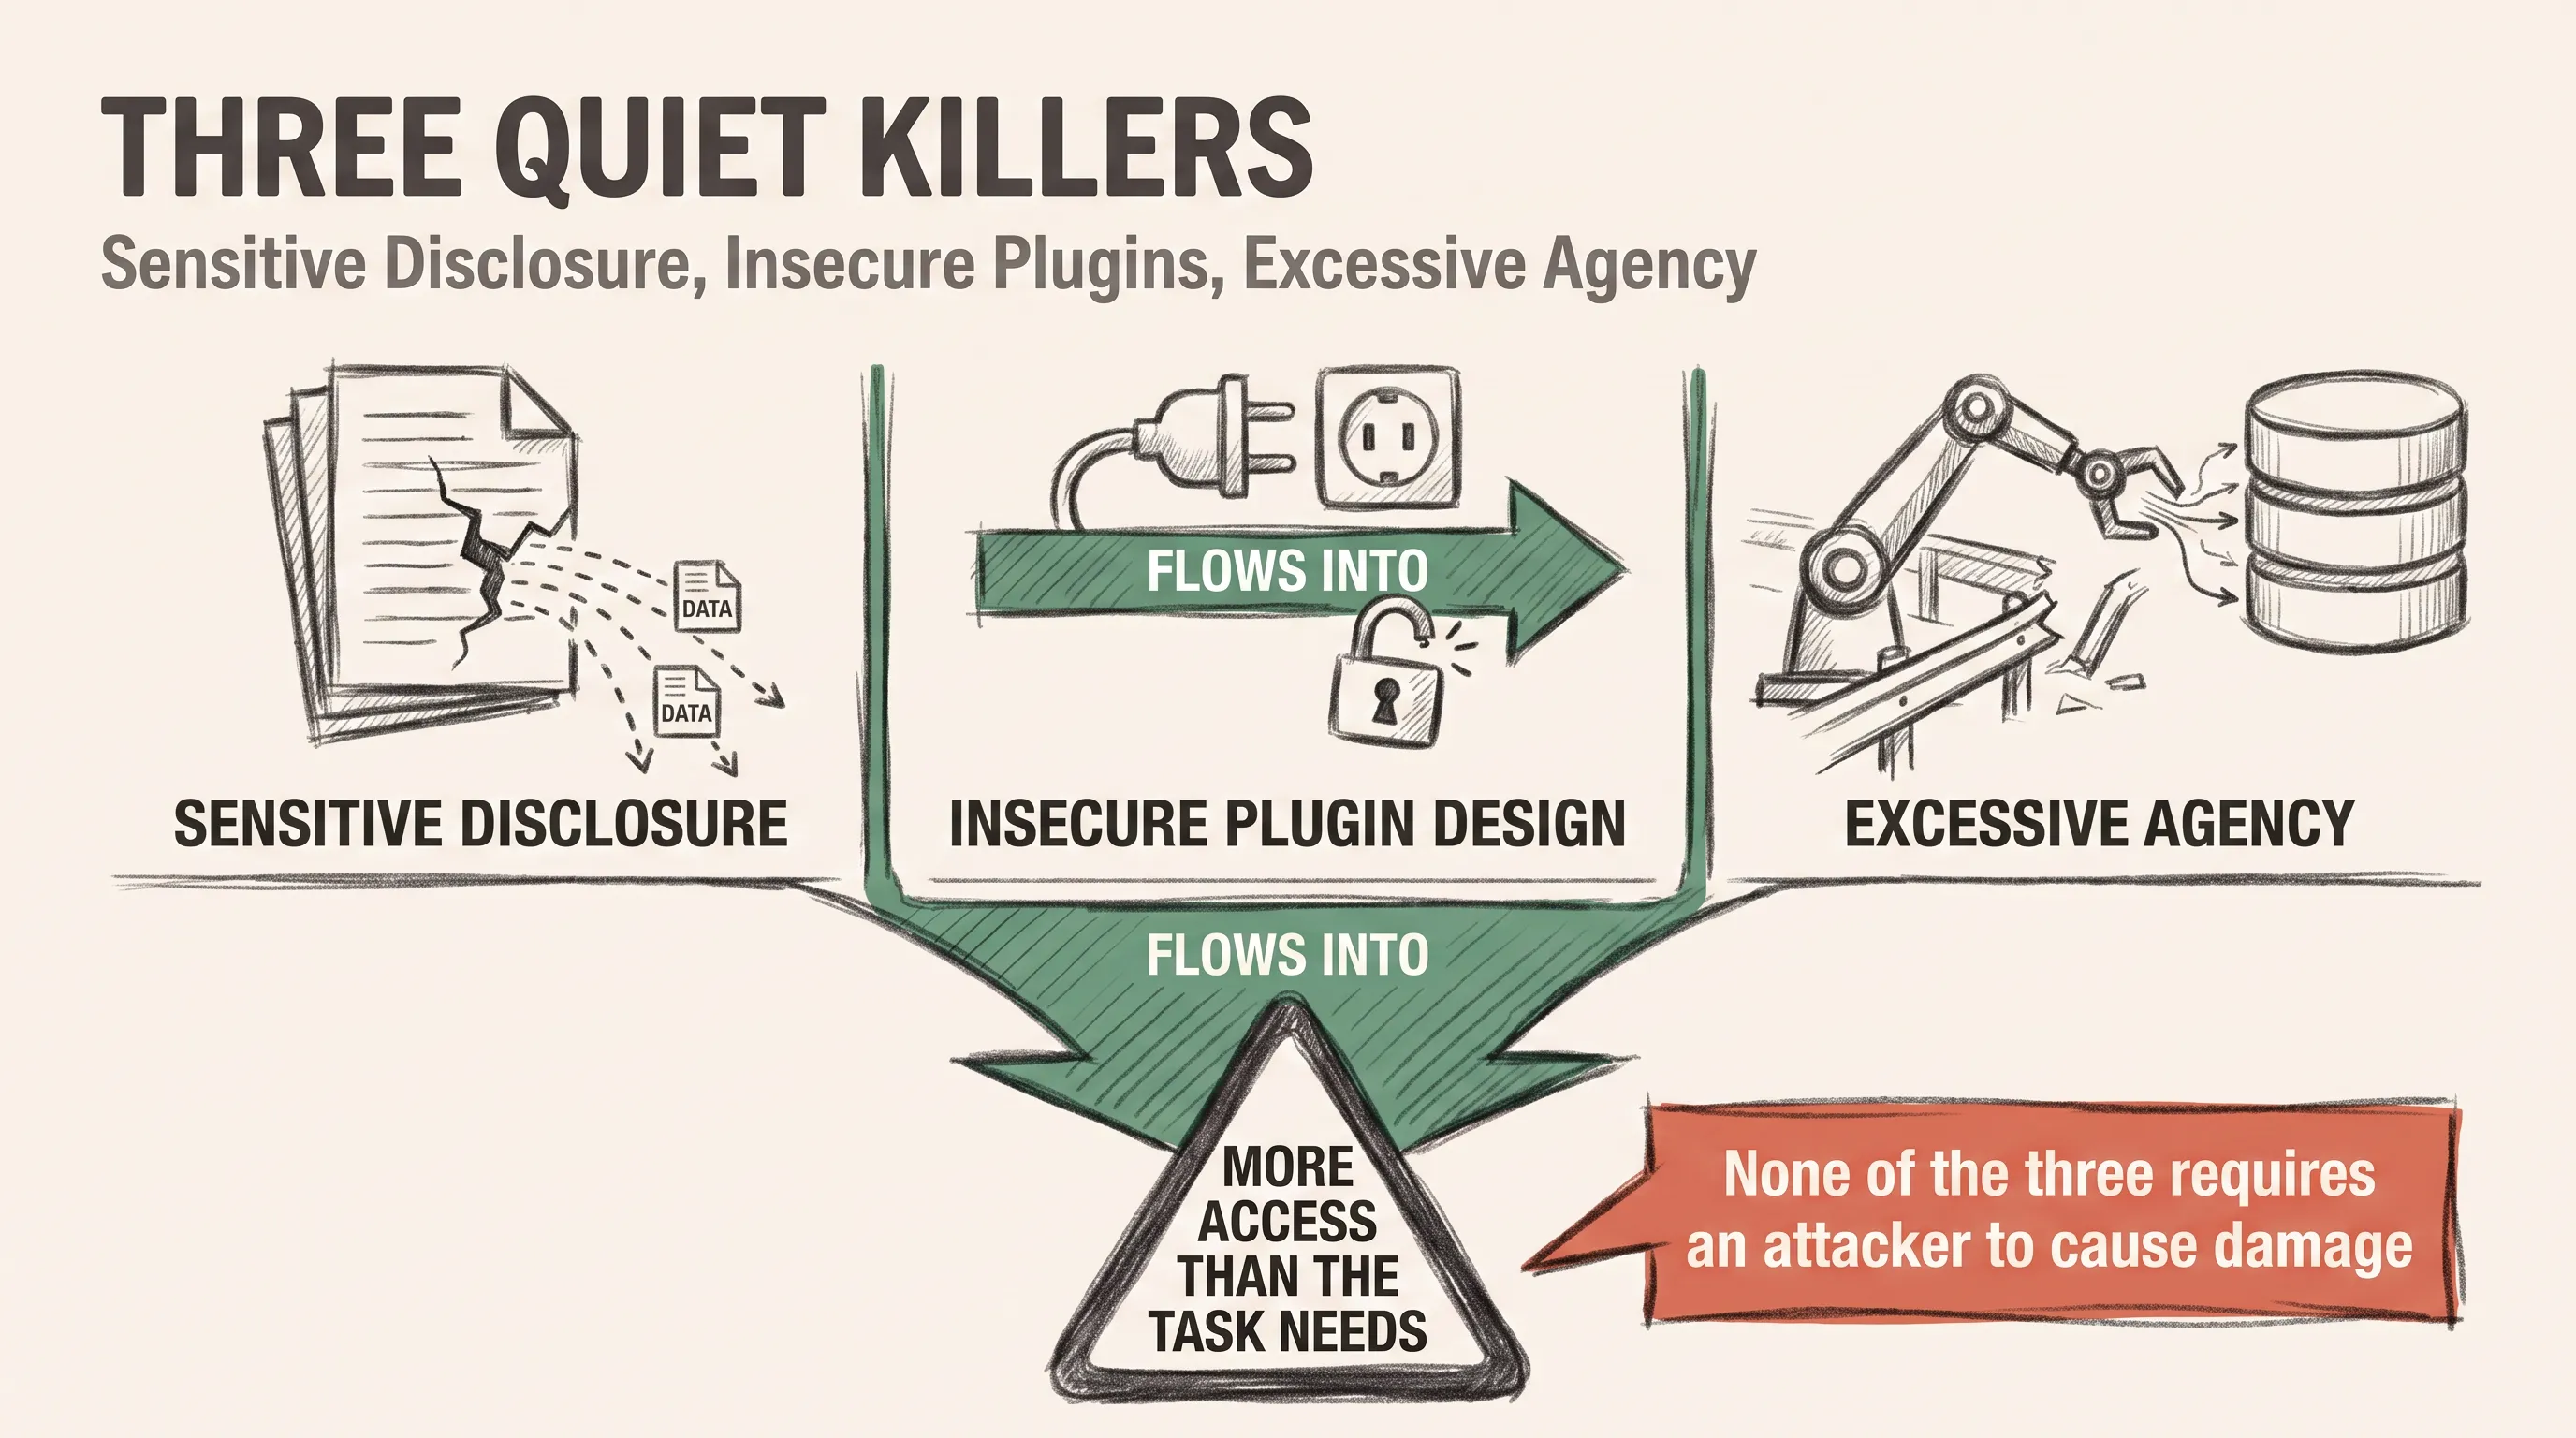 llm-security8 min read
Three Quiet Killers: Sensitive Disclosure, Insecure Plugins, Excessive Agency
Three under-discussed OWASP LLM risks: sensitive data leakage, insecure plugin design, and excessive agent autonomy, with mitigations for each.
-
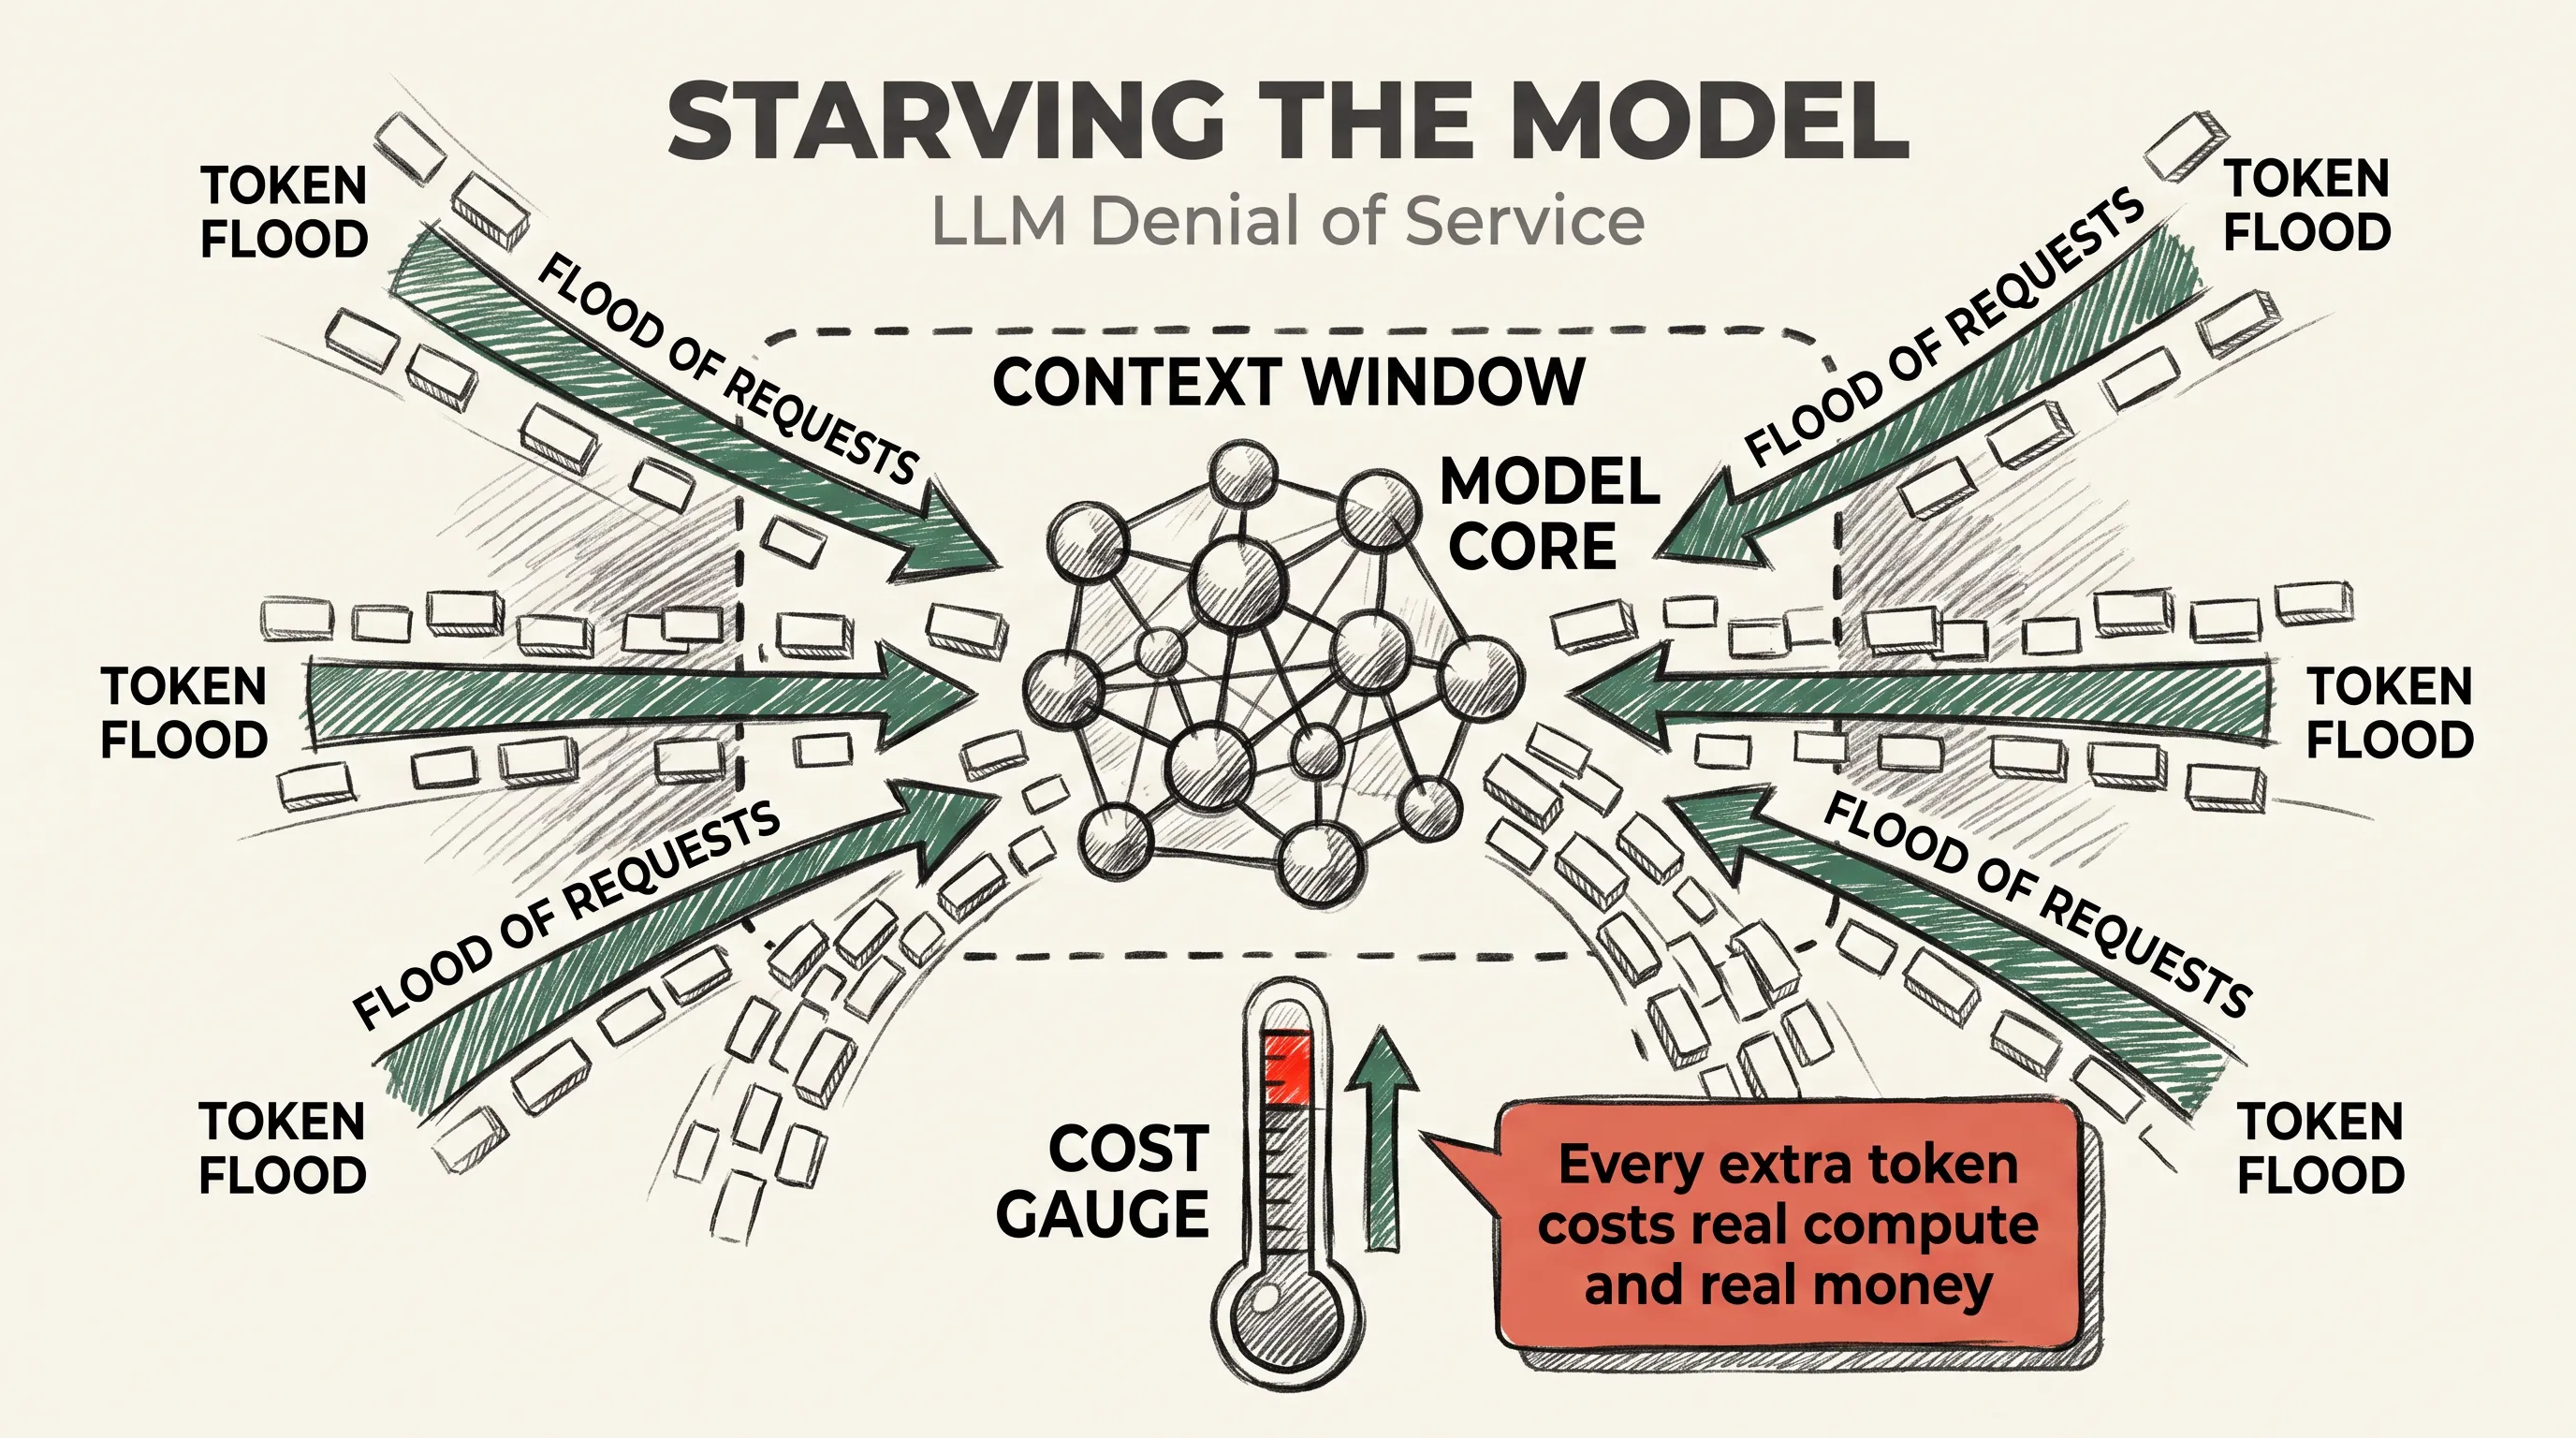 llm-security6 min read
Starving the Model: LLM Denial of Service
Context-window exhaustion and denial-of-wallet attacks against LLM applications, and the rate limiting, input caps, and resource budgeting that contain them.
-
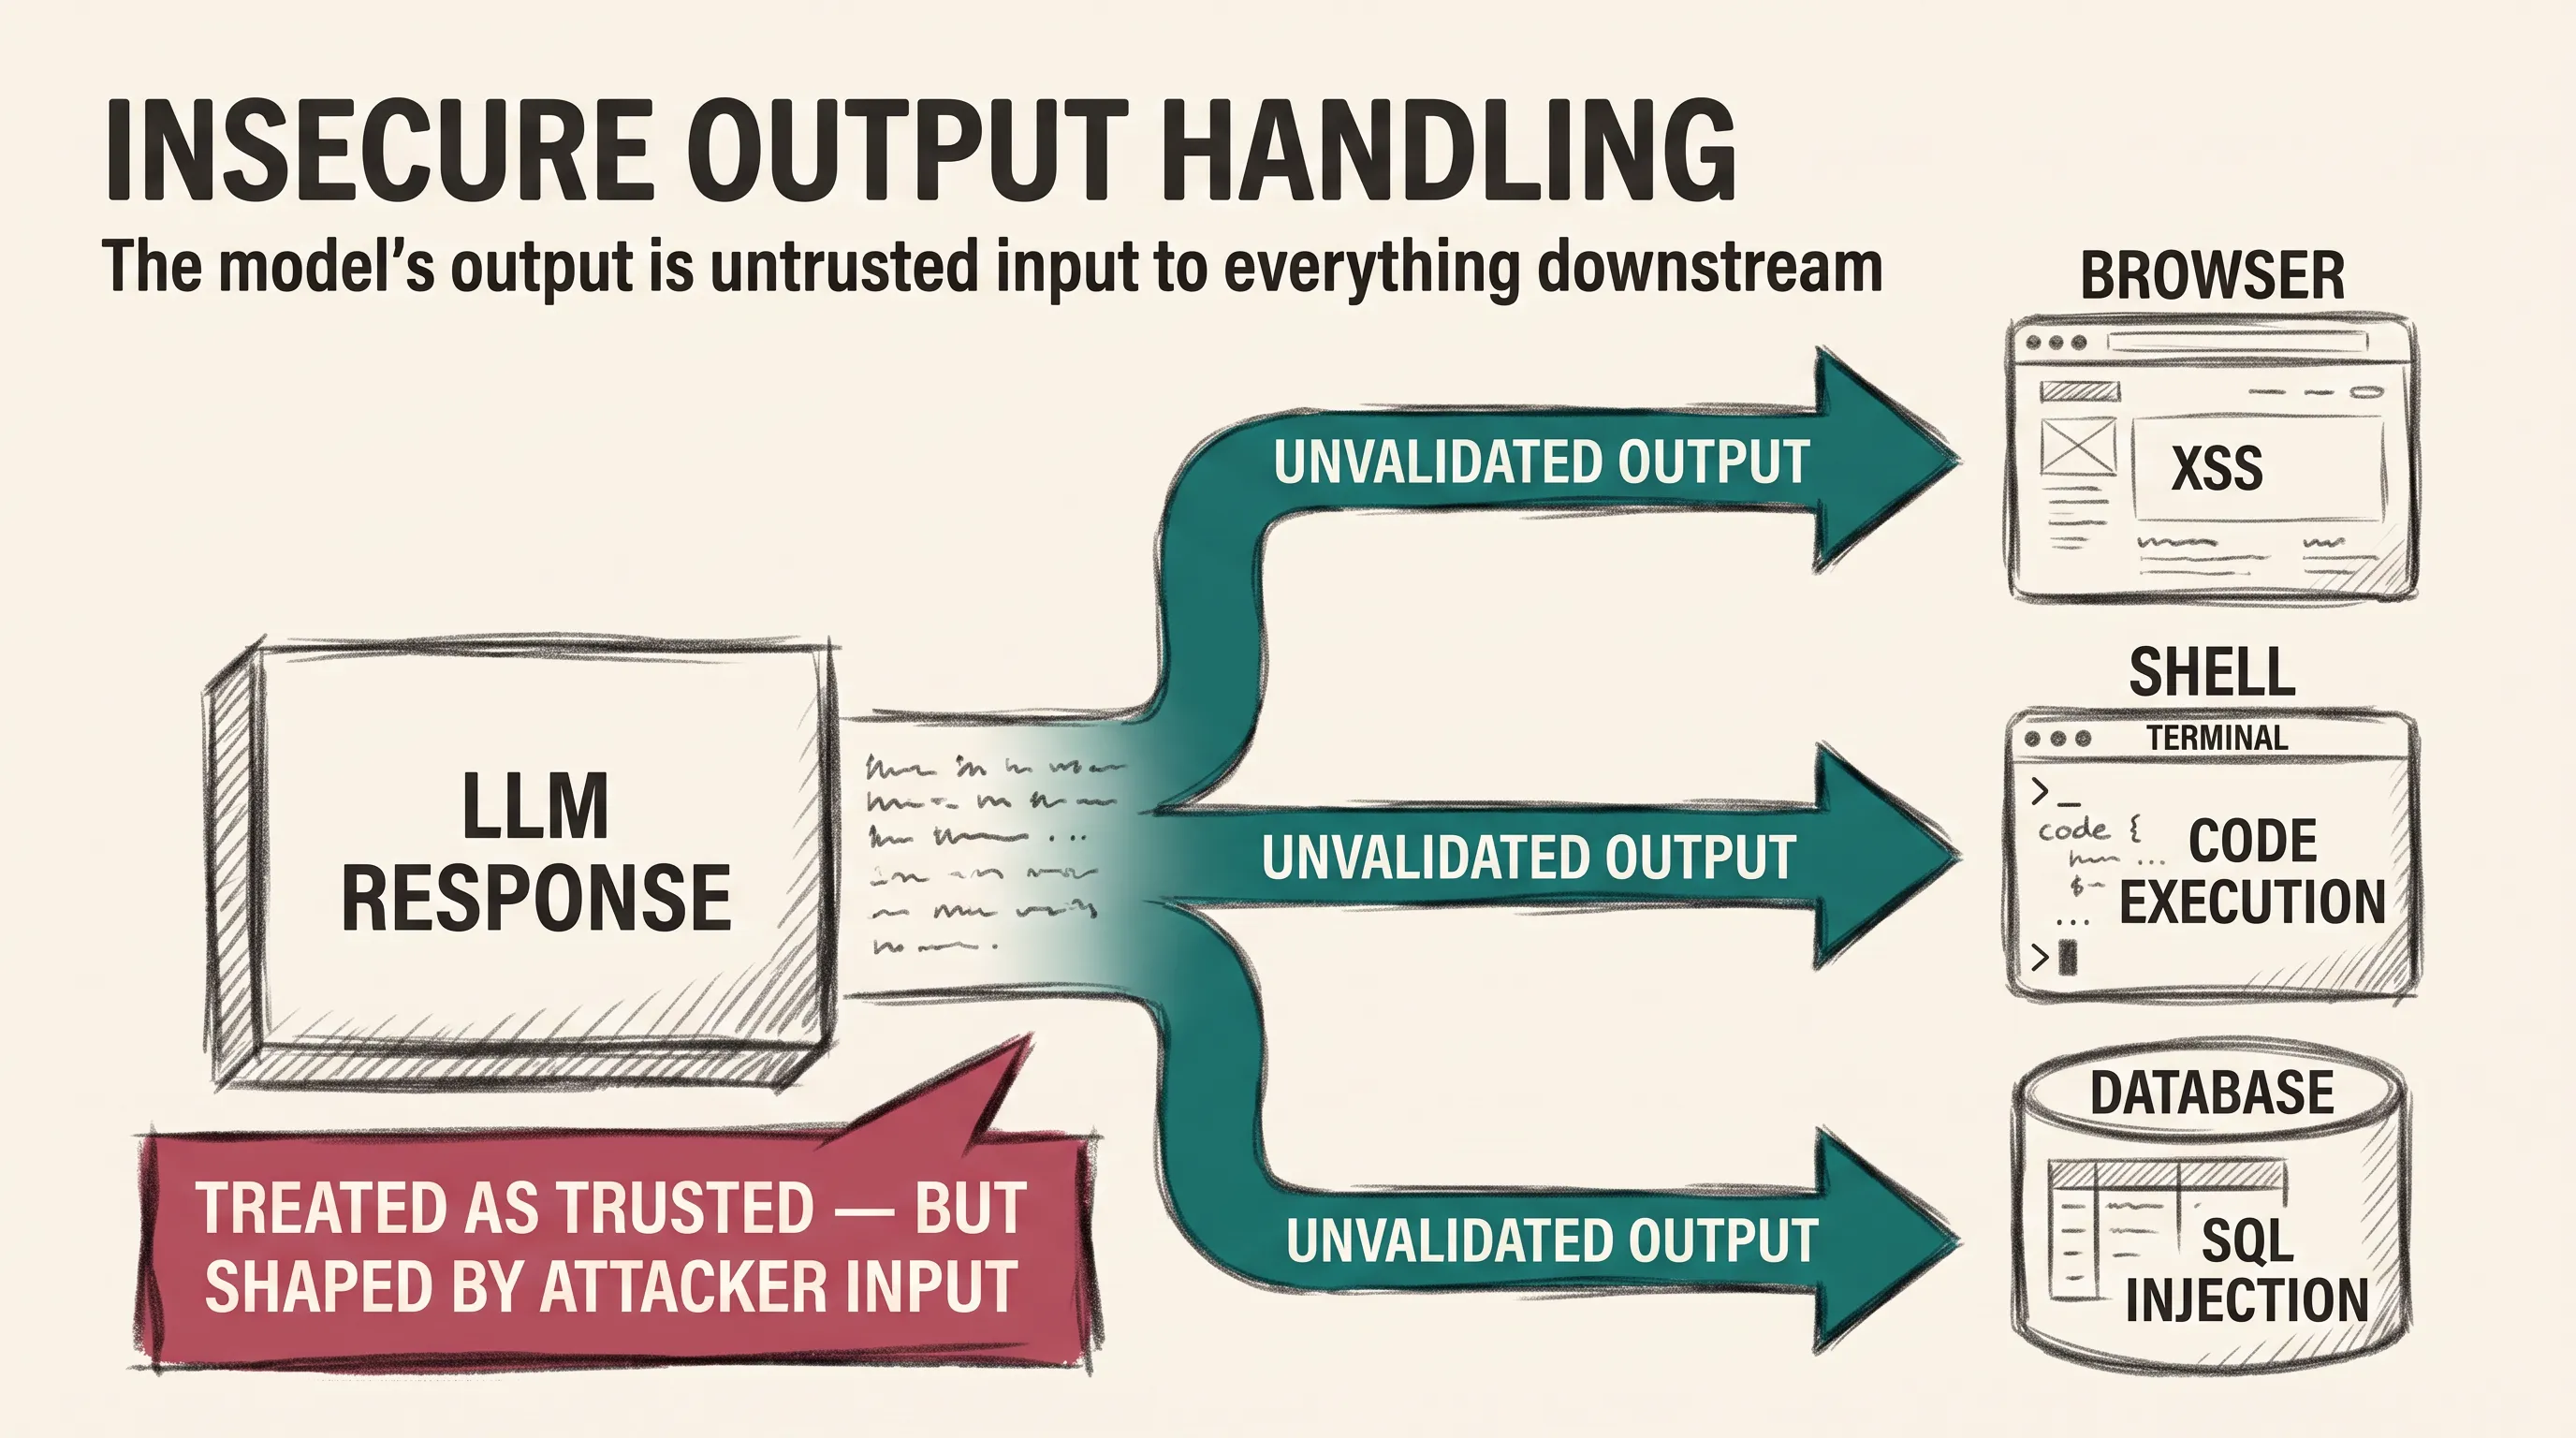 llm-security8 min read
Insecure Output Handling
Why model output must be treated as untrusted input, how it becomes XSS, SSRF, and code execution downstream, and the encoding and validation that contain it.
-
 llm-security7 min read
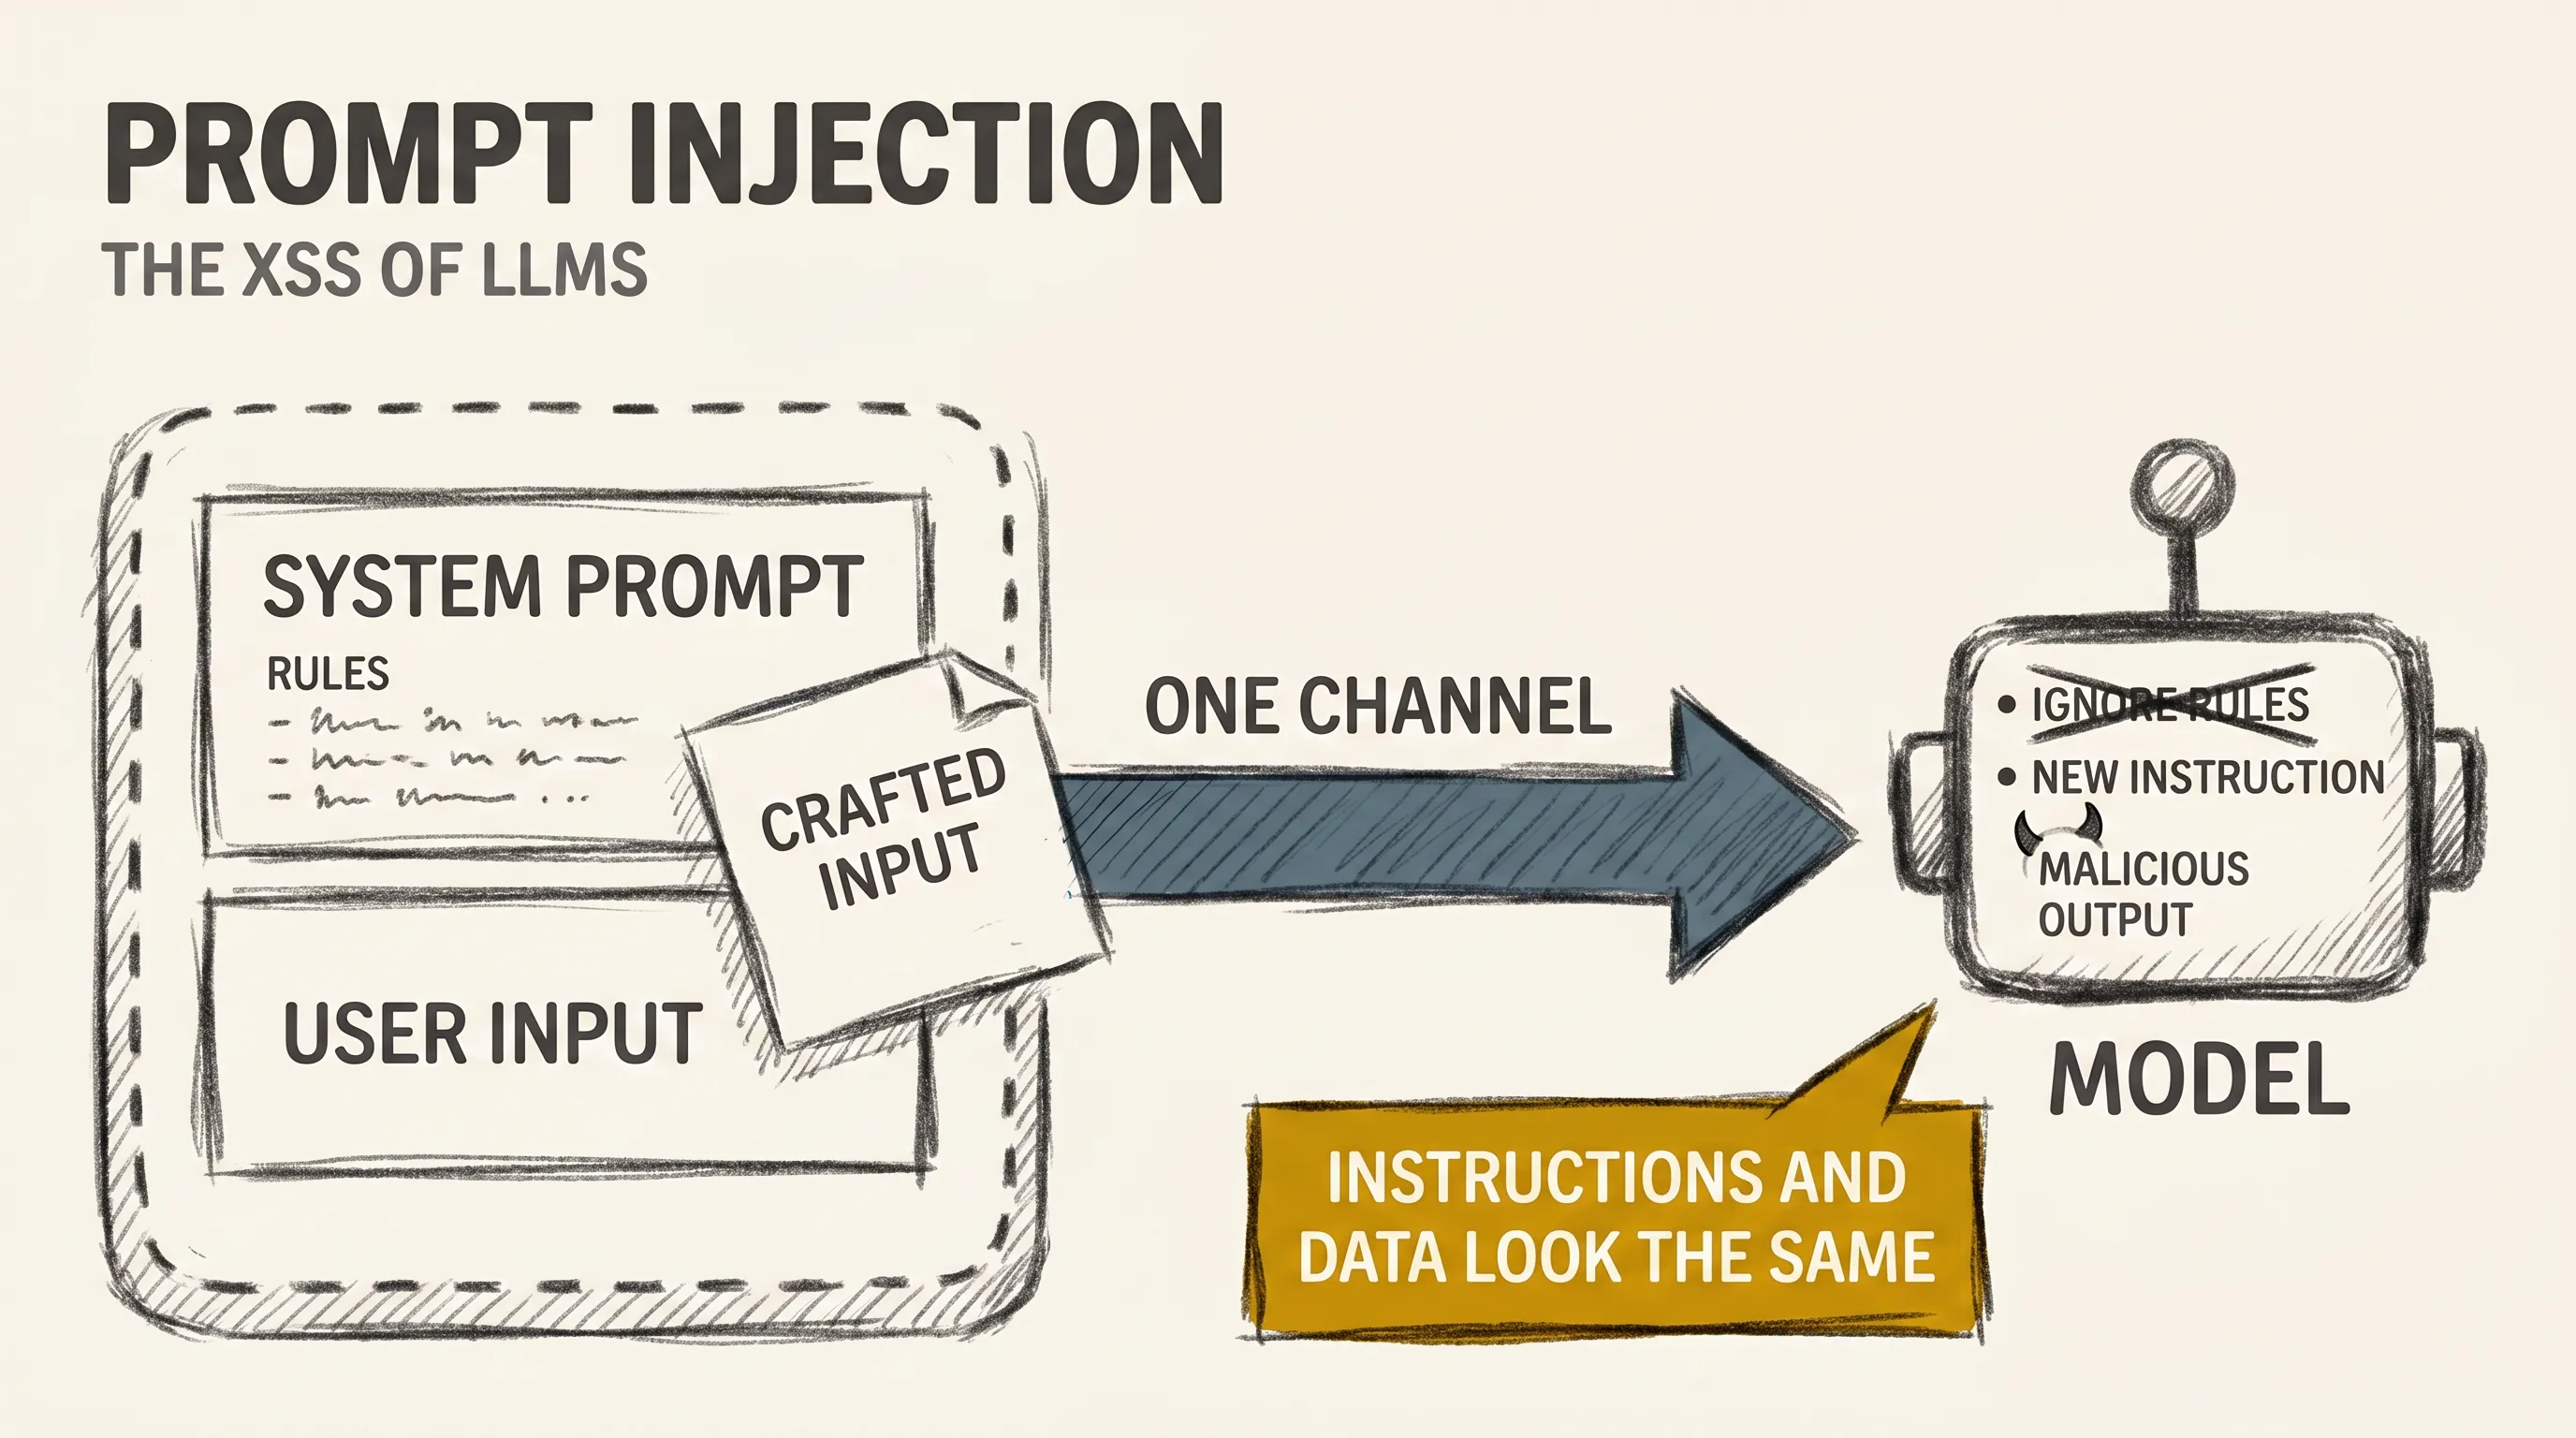
Prompt Injection: The XSS of LLMs
How prompt injection subverts large language models through direct and indirect input, why it has no clean fix, and the layered defenses that contain it.
-
 llm-security9 min read
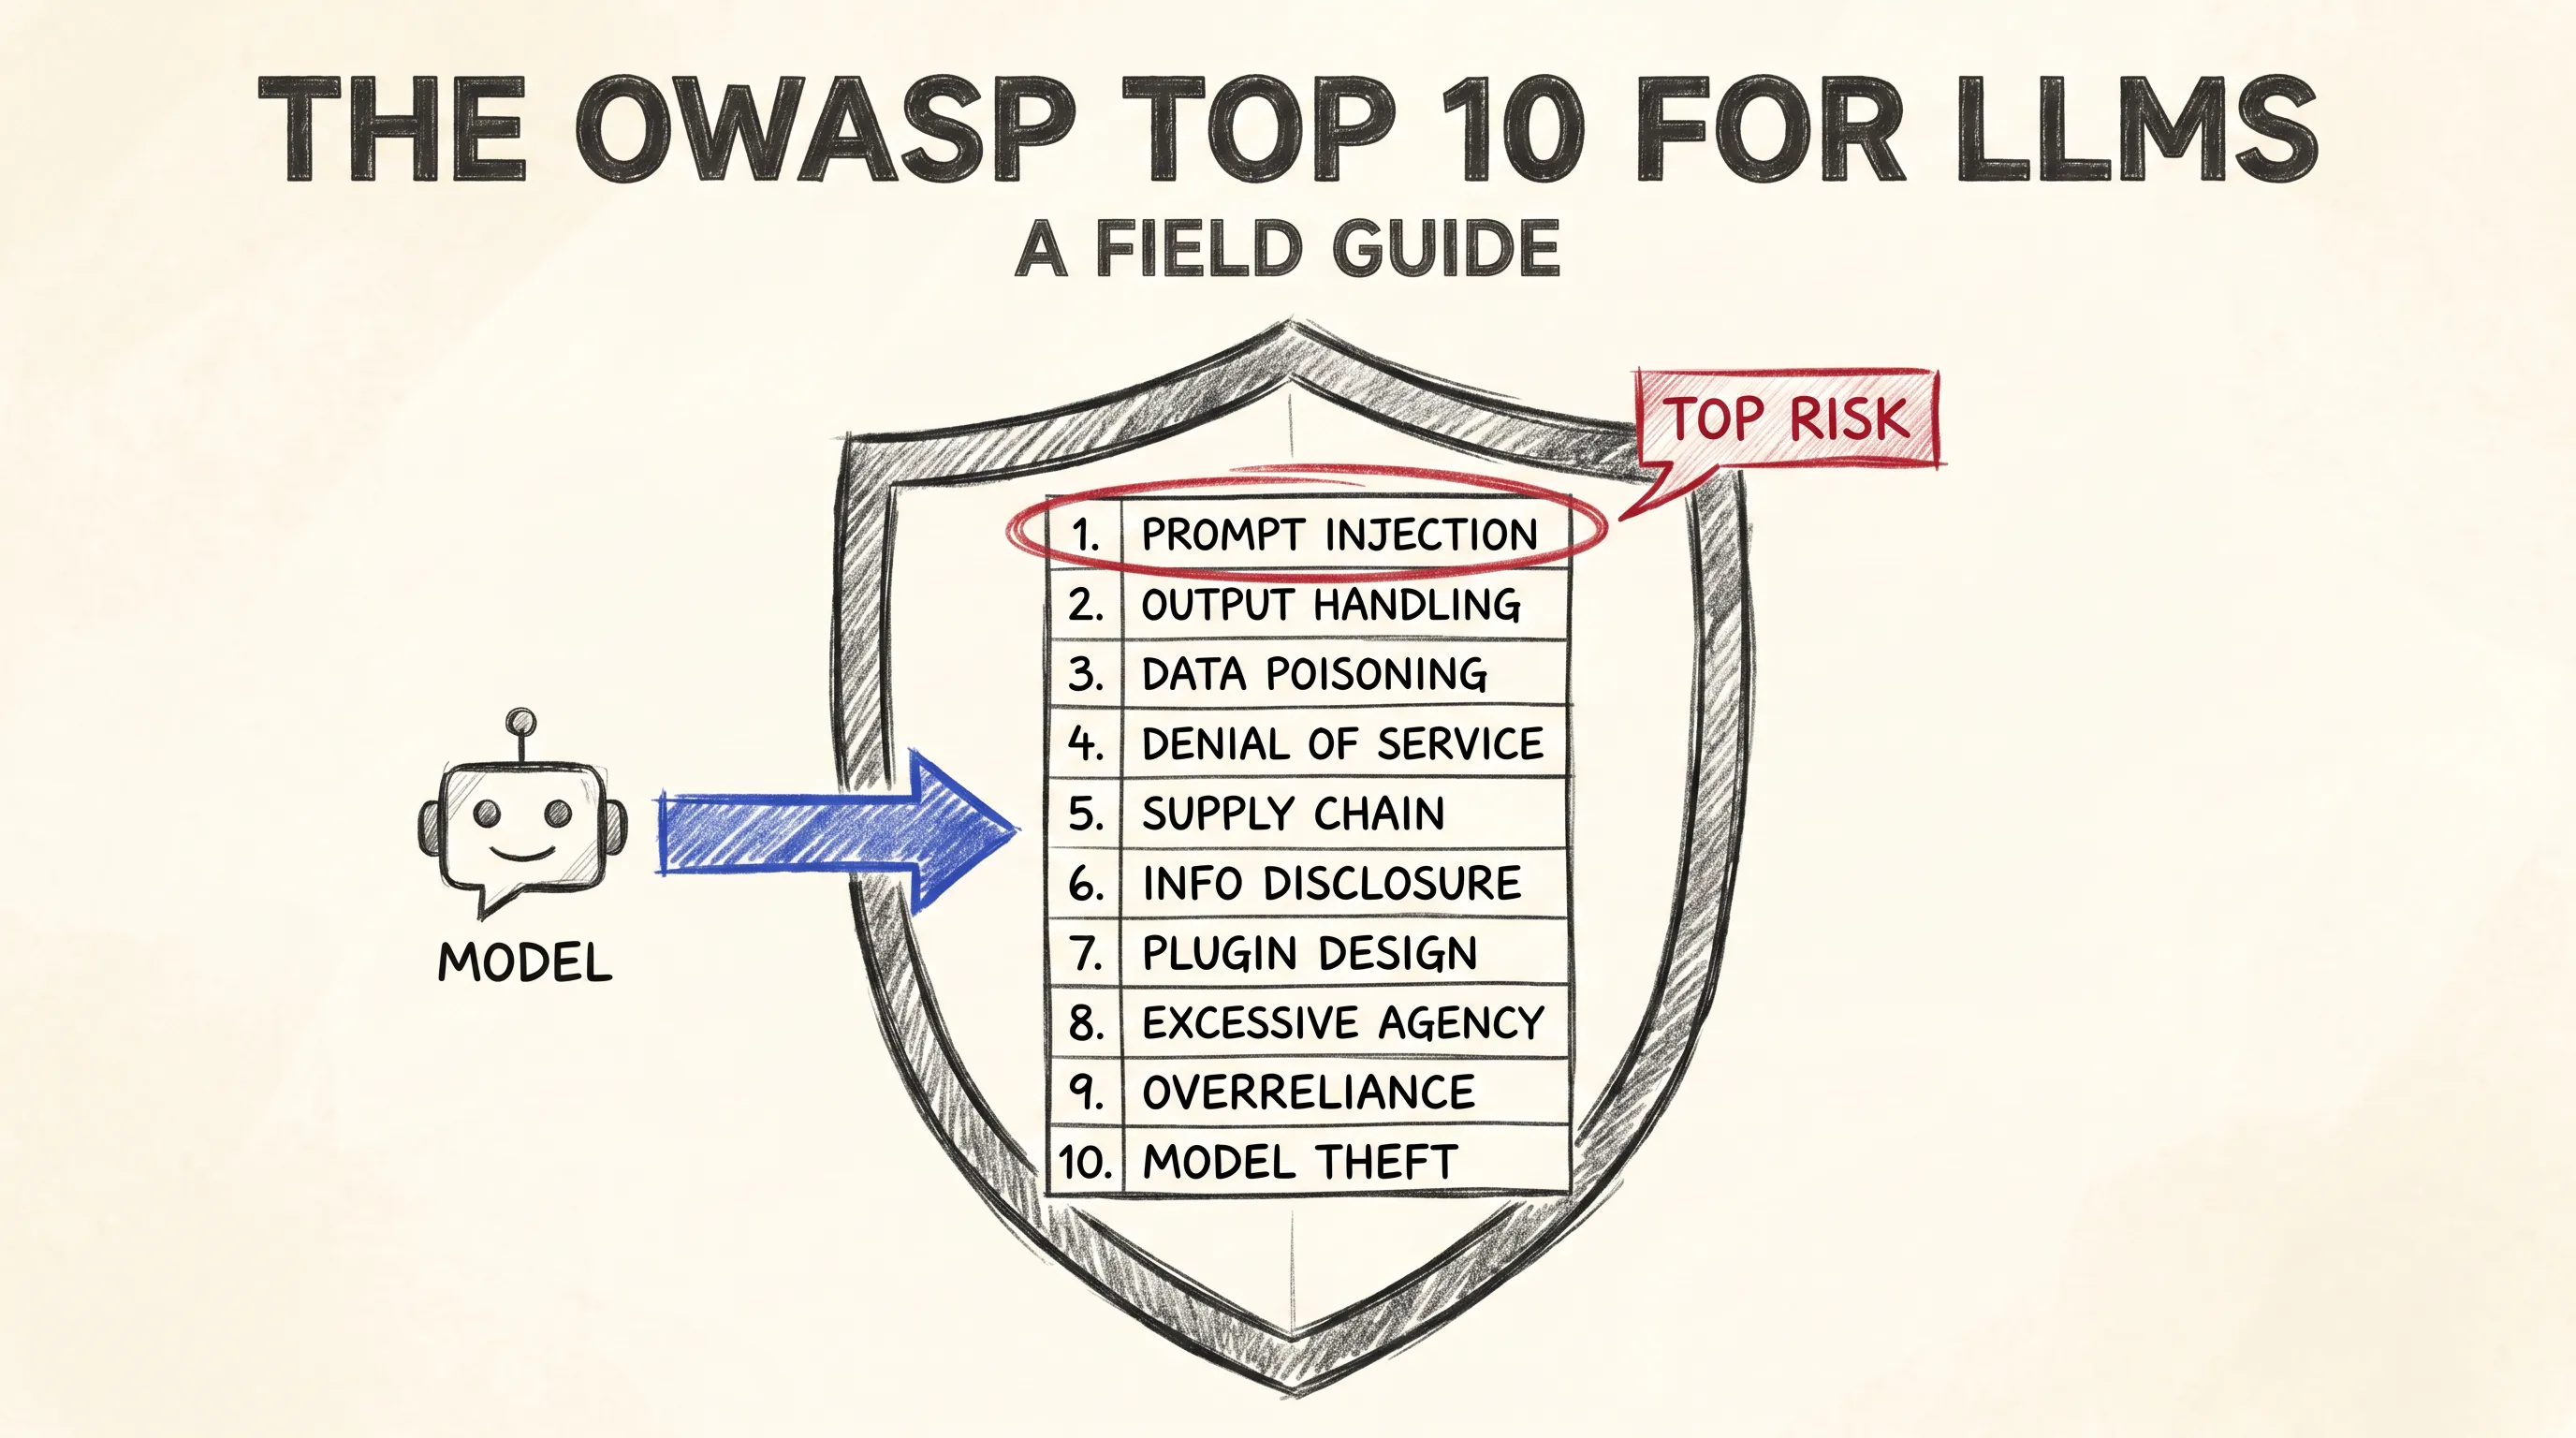
The OWASP Top 10 for LLMs: A Field Guide
A field guide to the OWASP Top 10 for LLM Applications, the ten vulnerability categories that define modern AI application security.