Tag: llm
All the articles with the tag "llm".
-
 llm-security6 min read
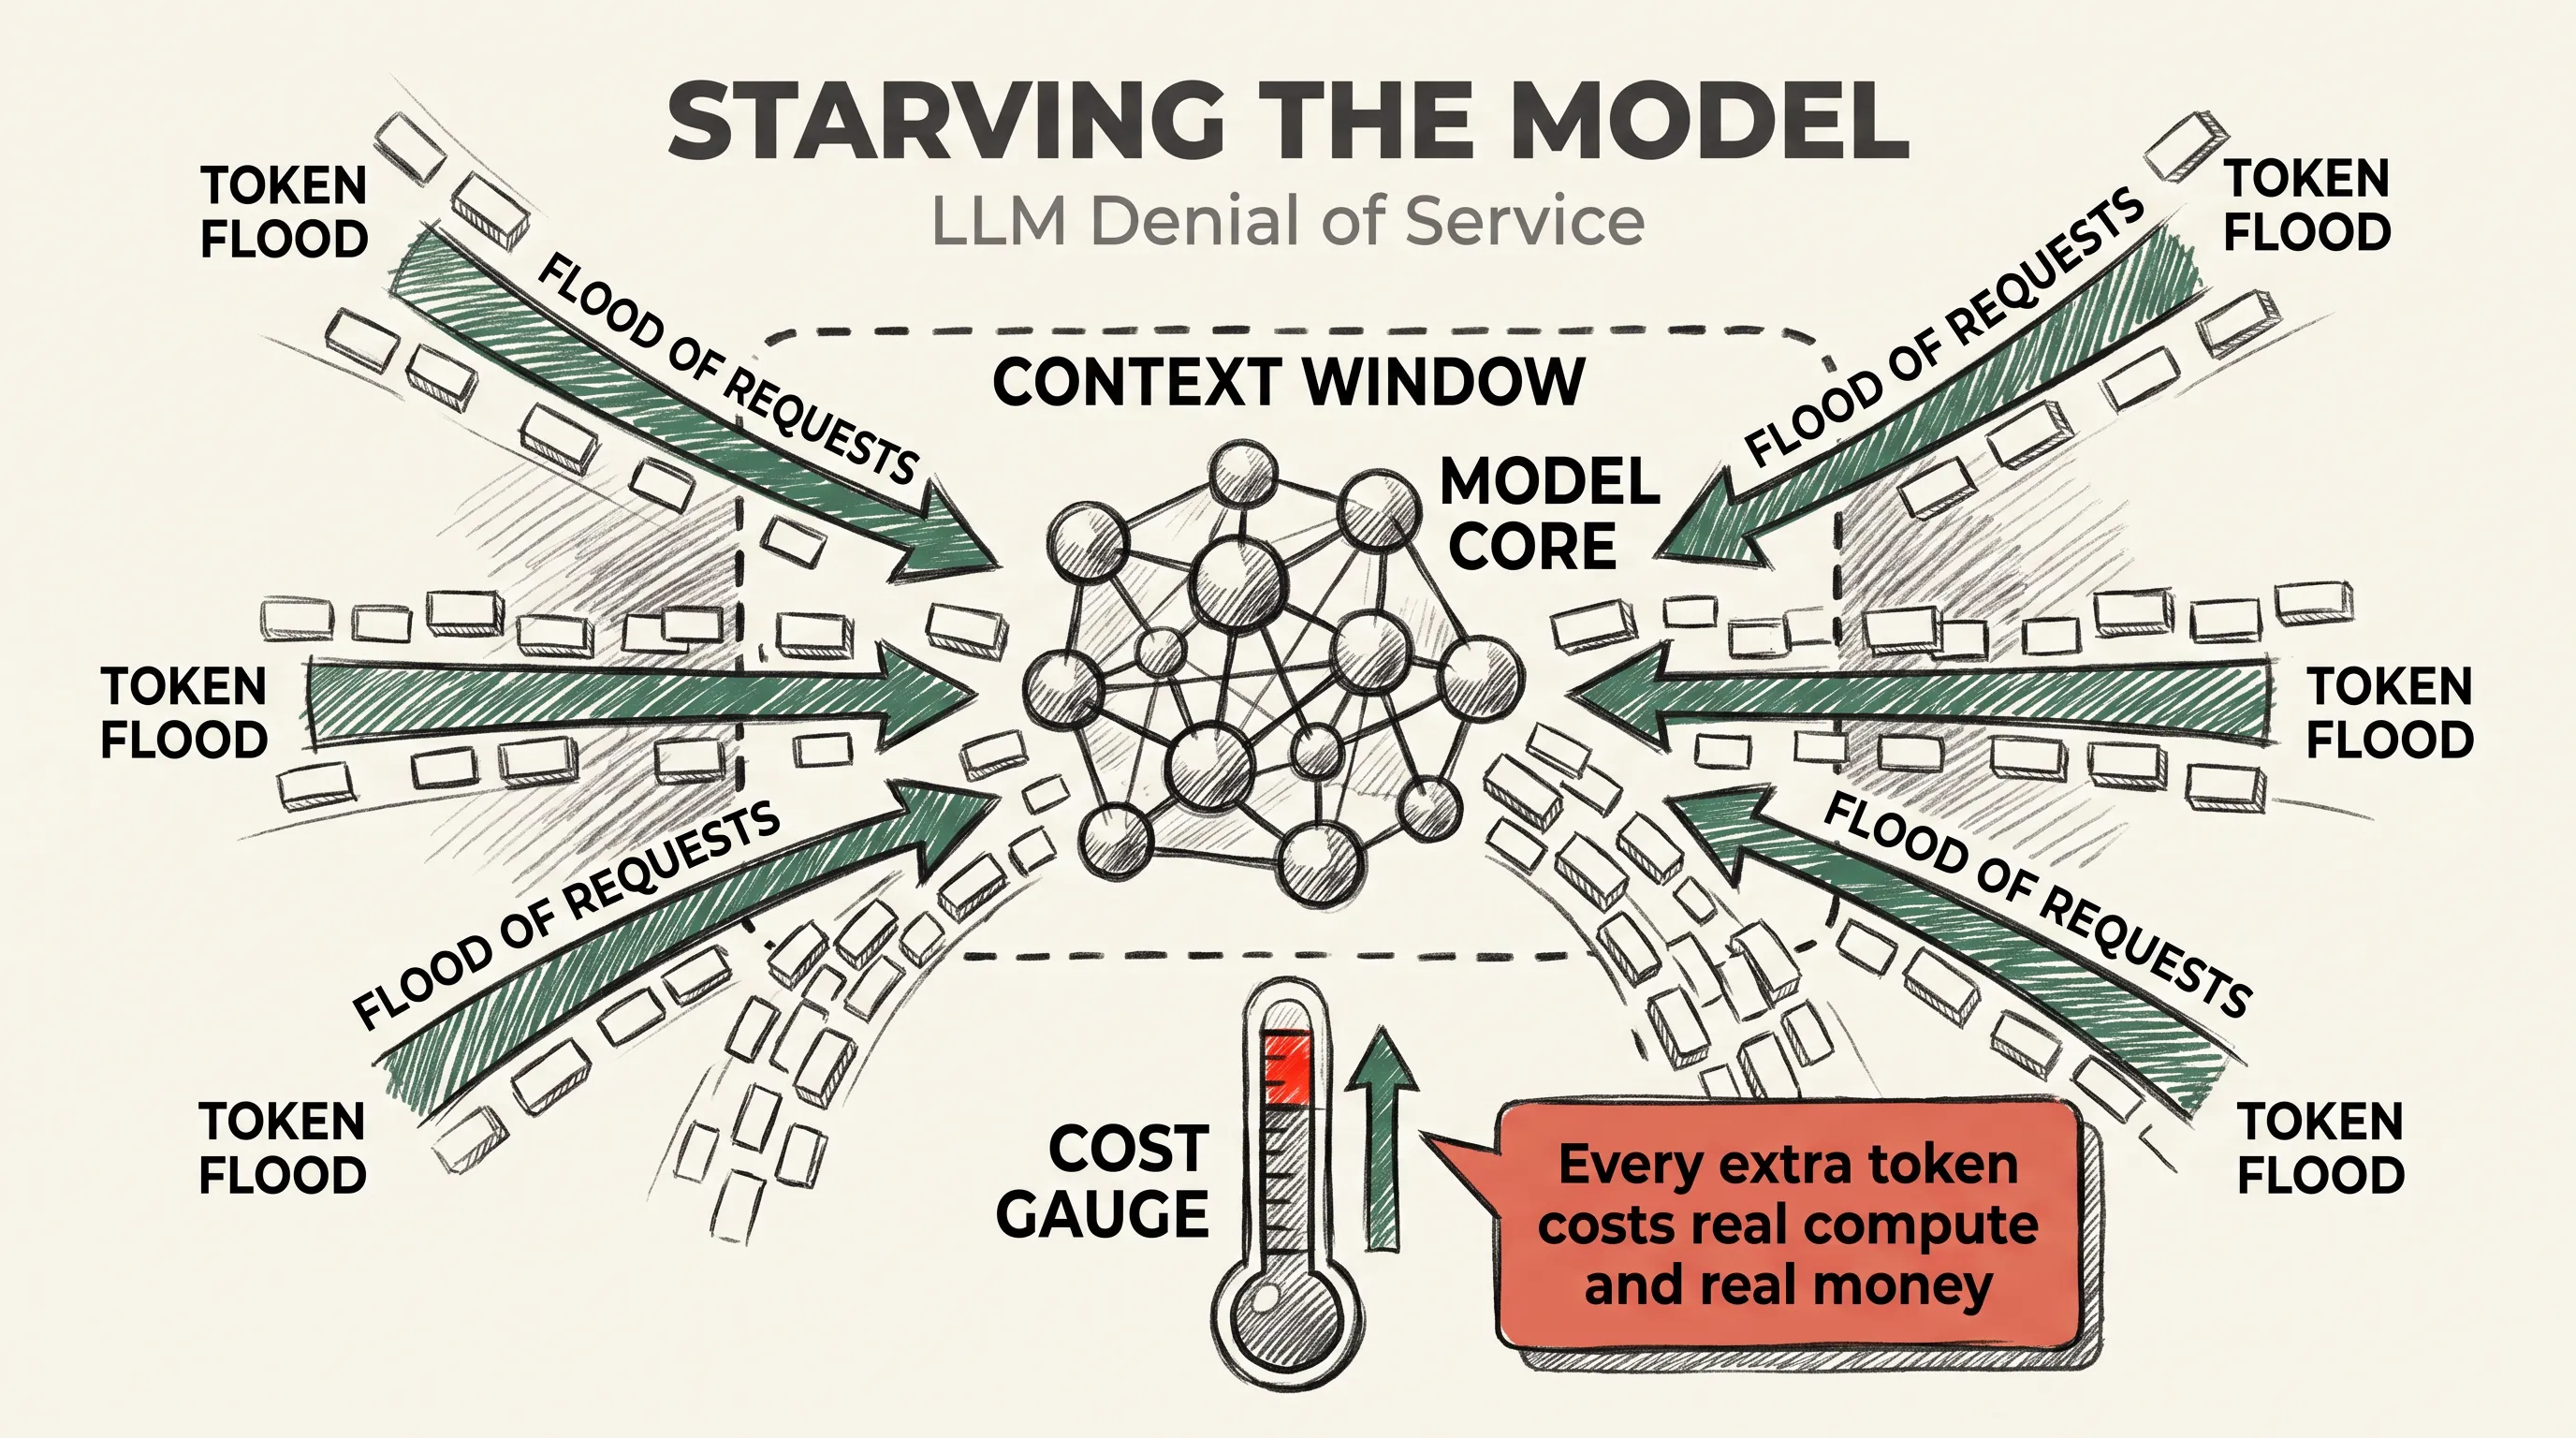
Starving the Model: LLM Denial of Service
Context-window exhaustion and denial-of-wallet attacks against LLM applications, and the rate limiting, input caps, and resource budgeting that contain them.
-
 llm-security7 min read
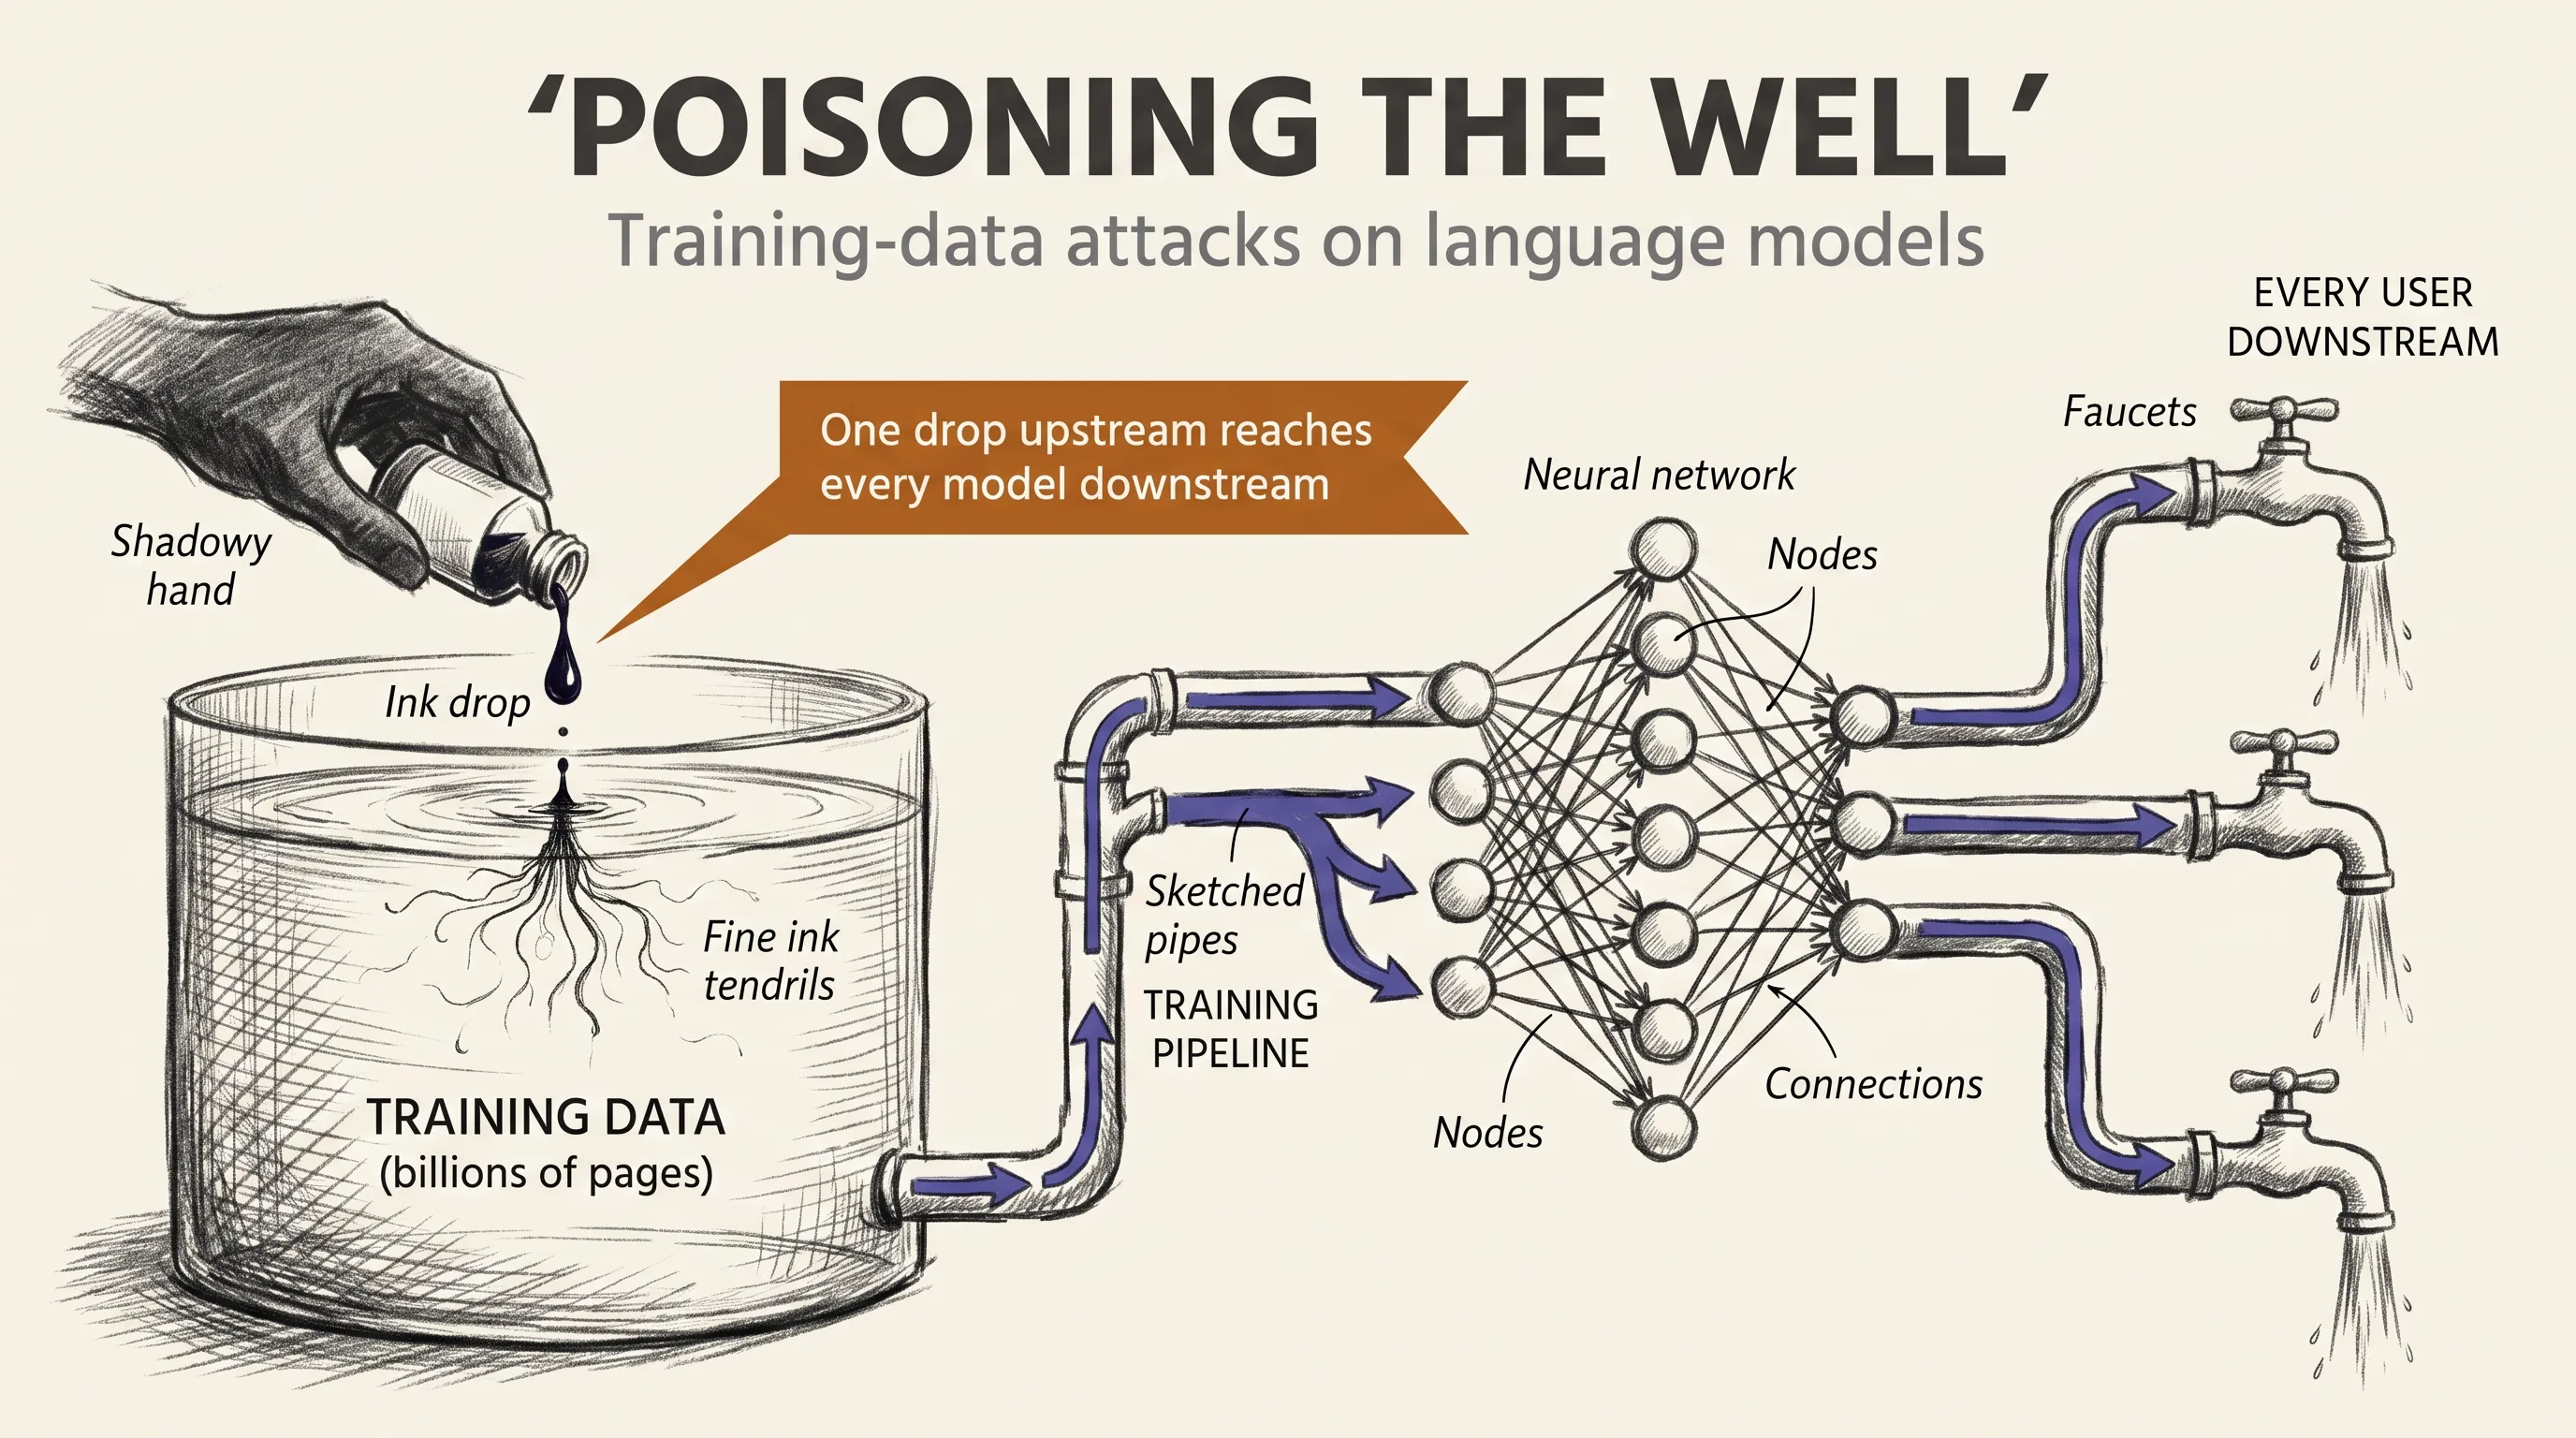
Poisoning the Well: Training-Data Attacks
How poisoned training data plants backdoors and bias in language models, where it enters the pipeline, and the defenses that catch it early.
-
 llm-security8 min read
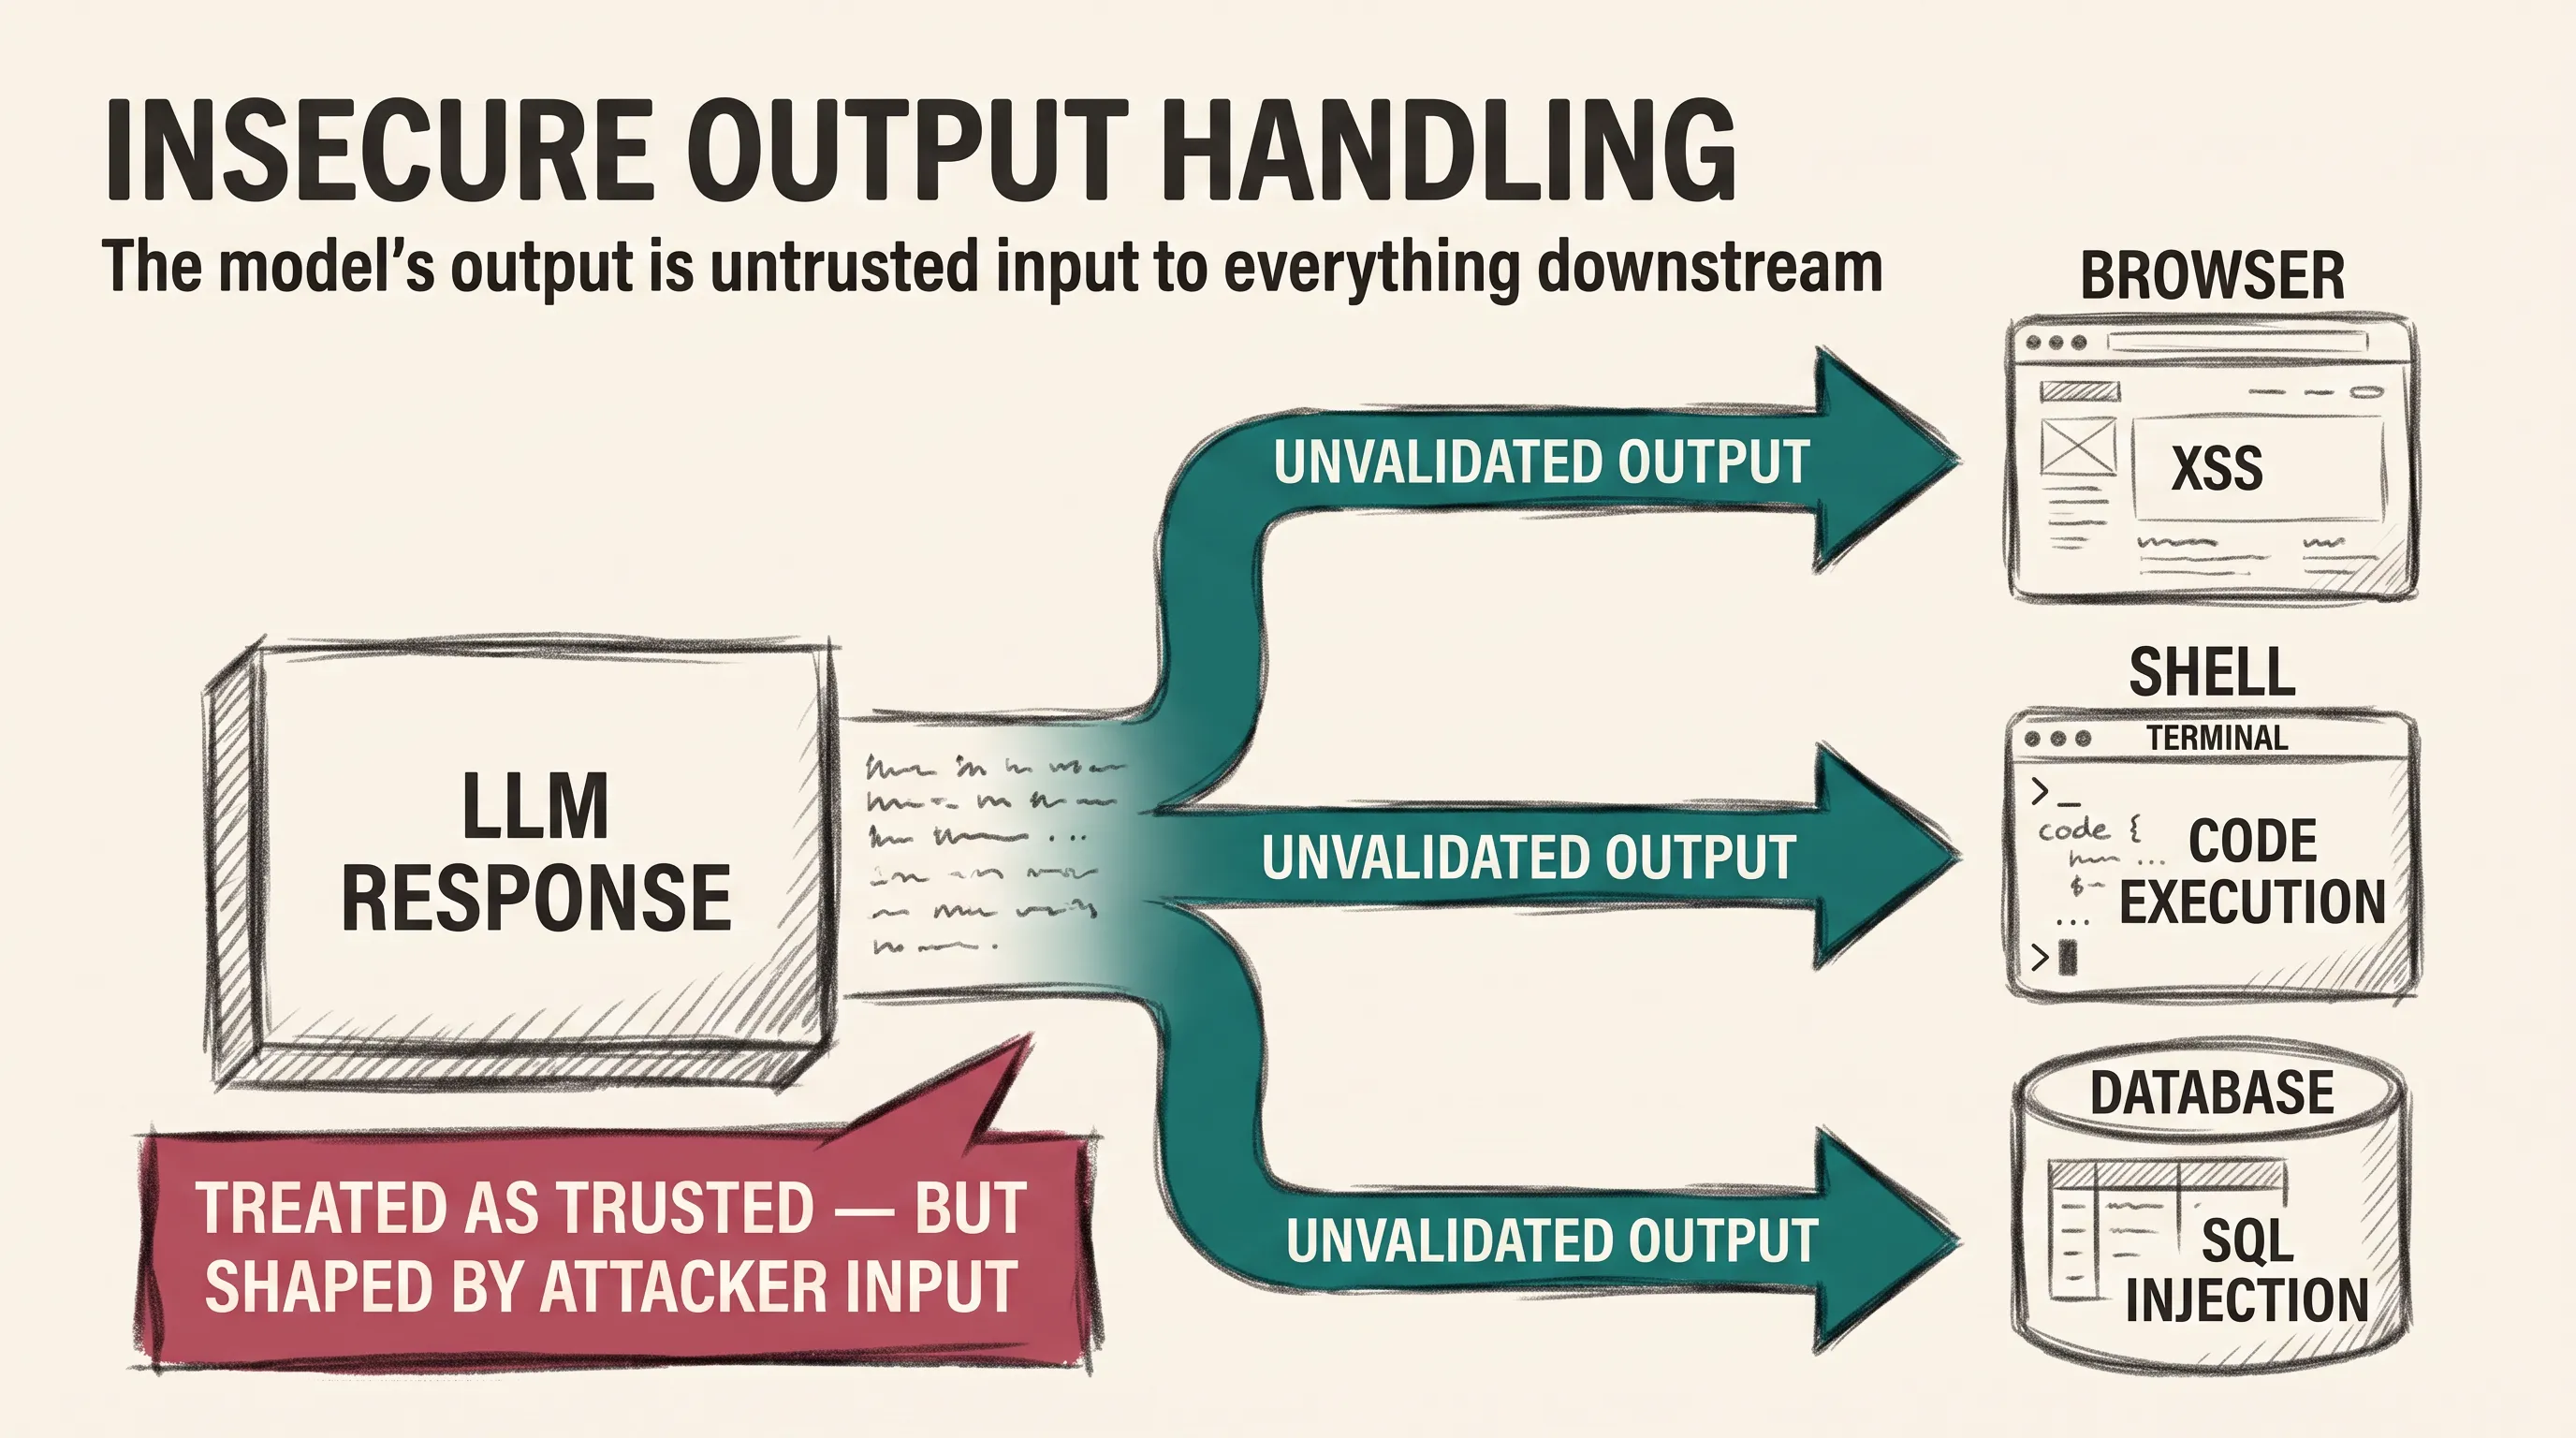
Insecure Output Handling
Why model output must be treated as untrusted input, how it becomes XSS, SSRF, and code execution downstream, and the encoding and validation that contain it.
-
 llm-security7 min read
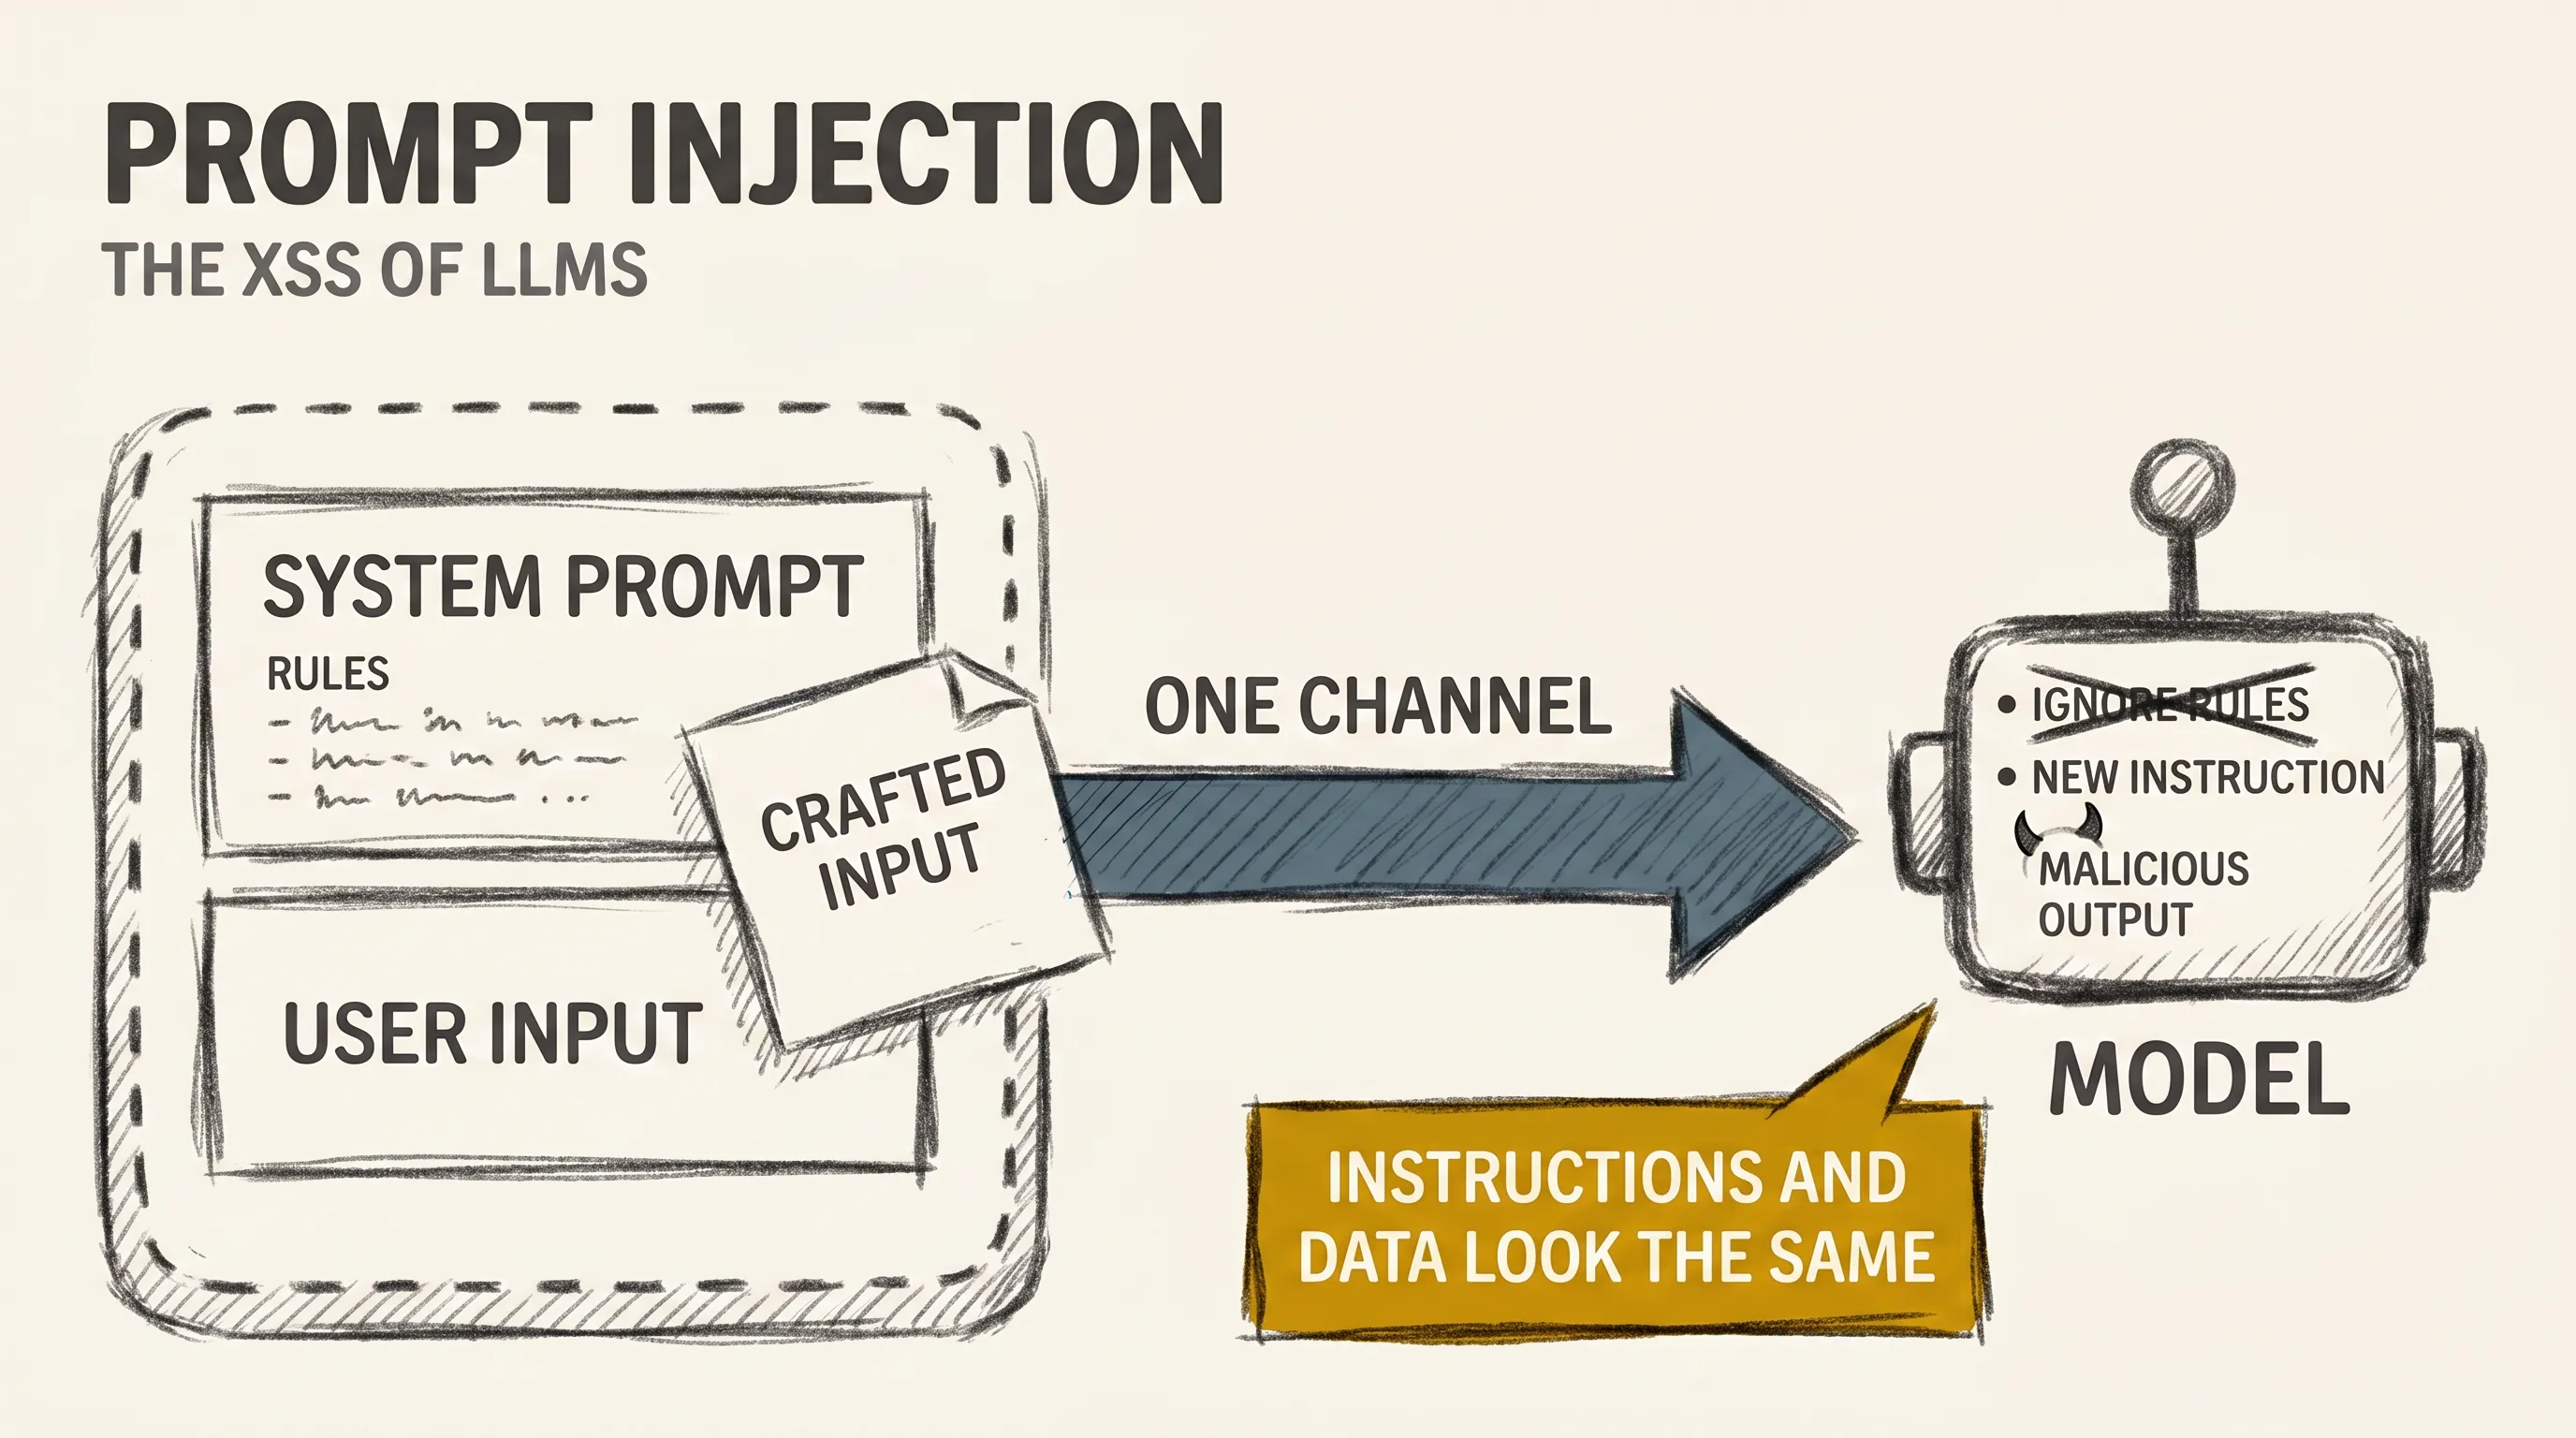
Prompt Injection: The XSS of LLMs
How prompt injection subverts large language models through direct and indirect input, why it has no clean fix, and the layered defenses that contain it.
-
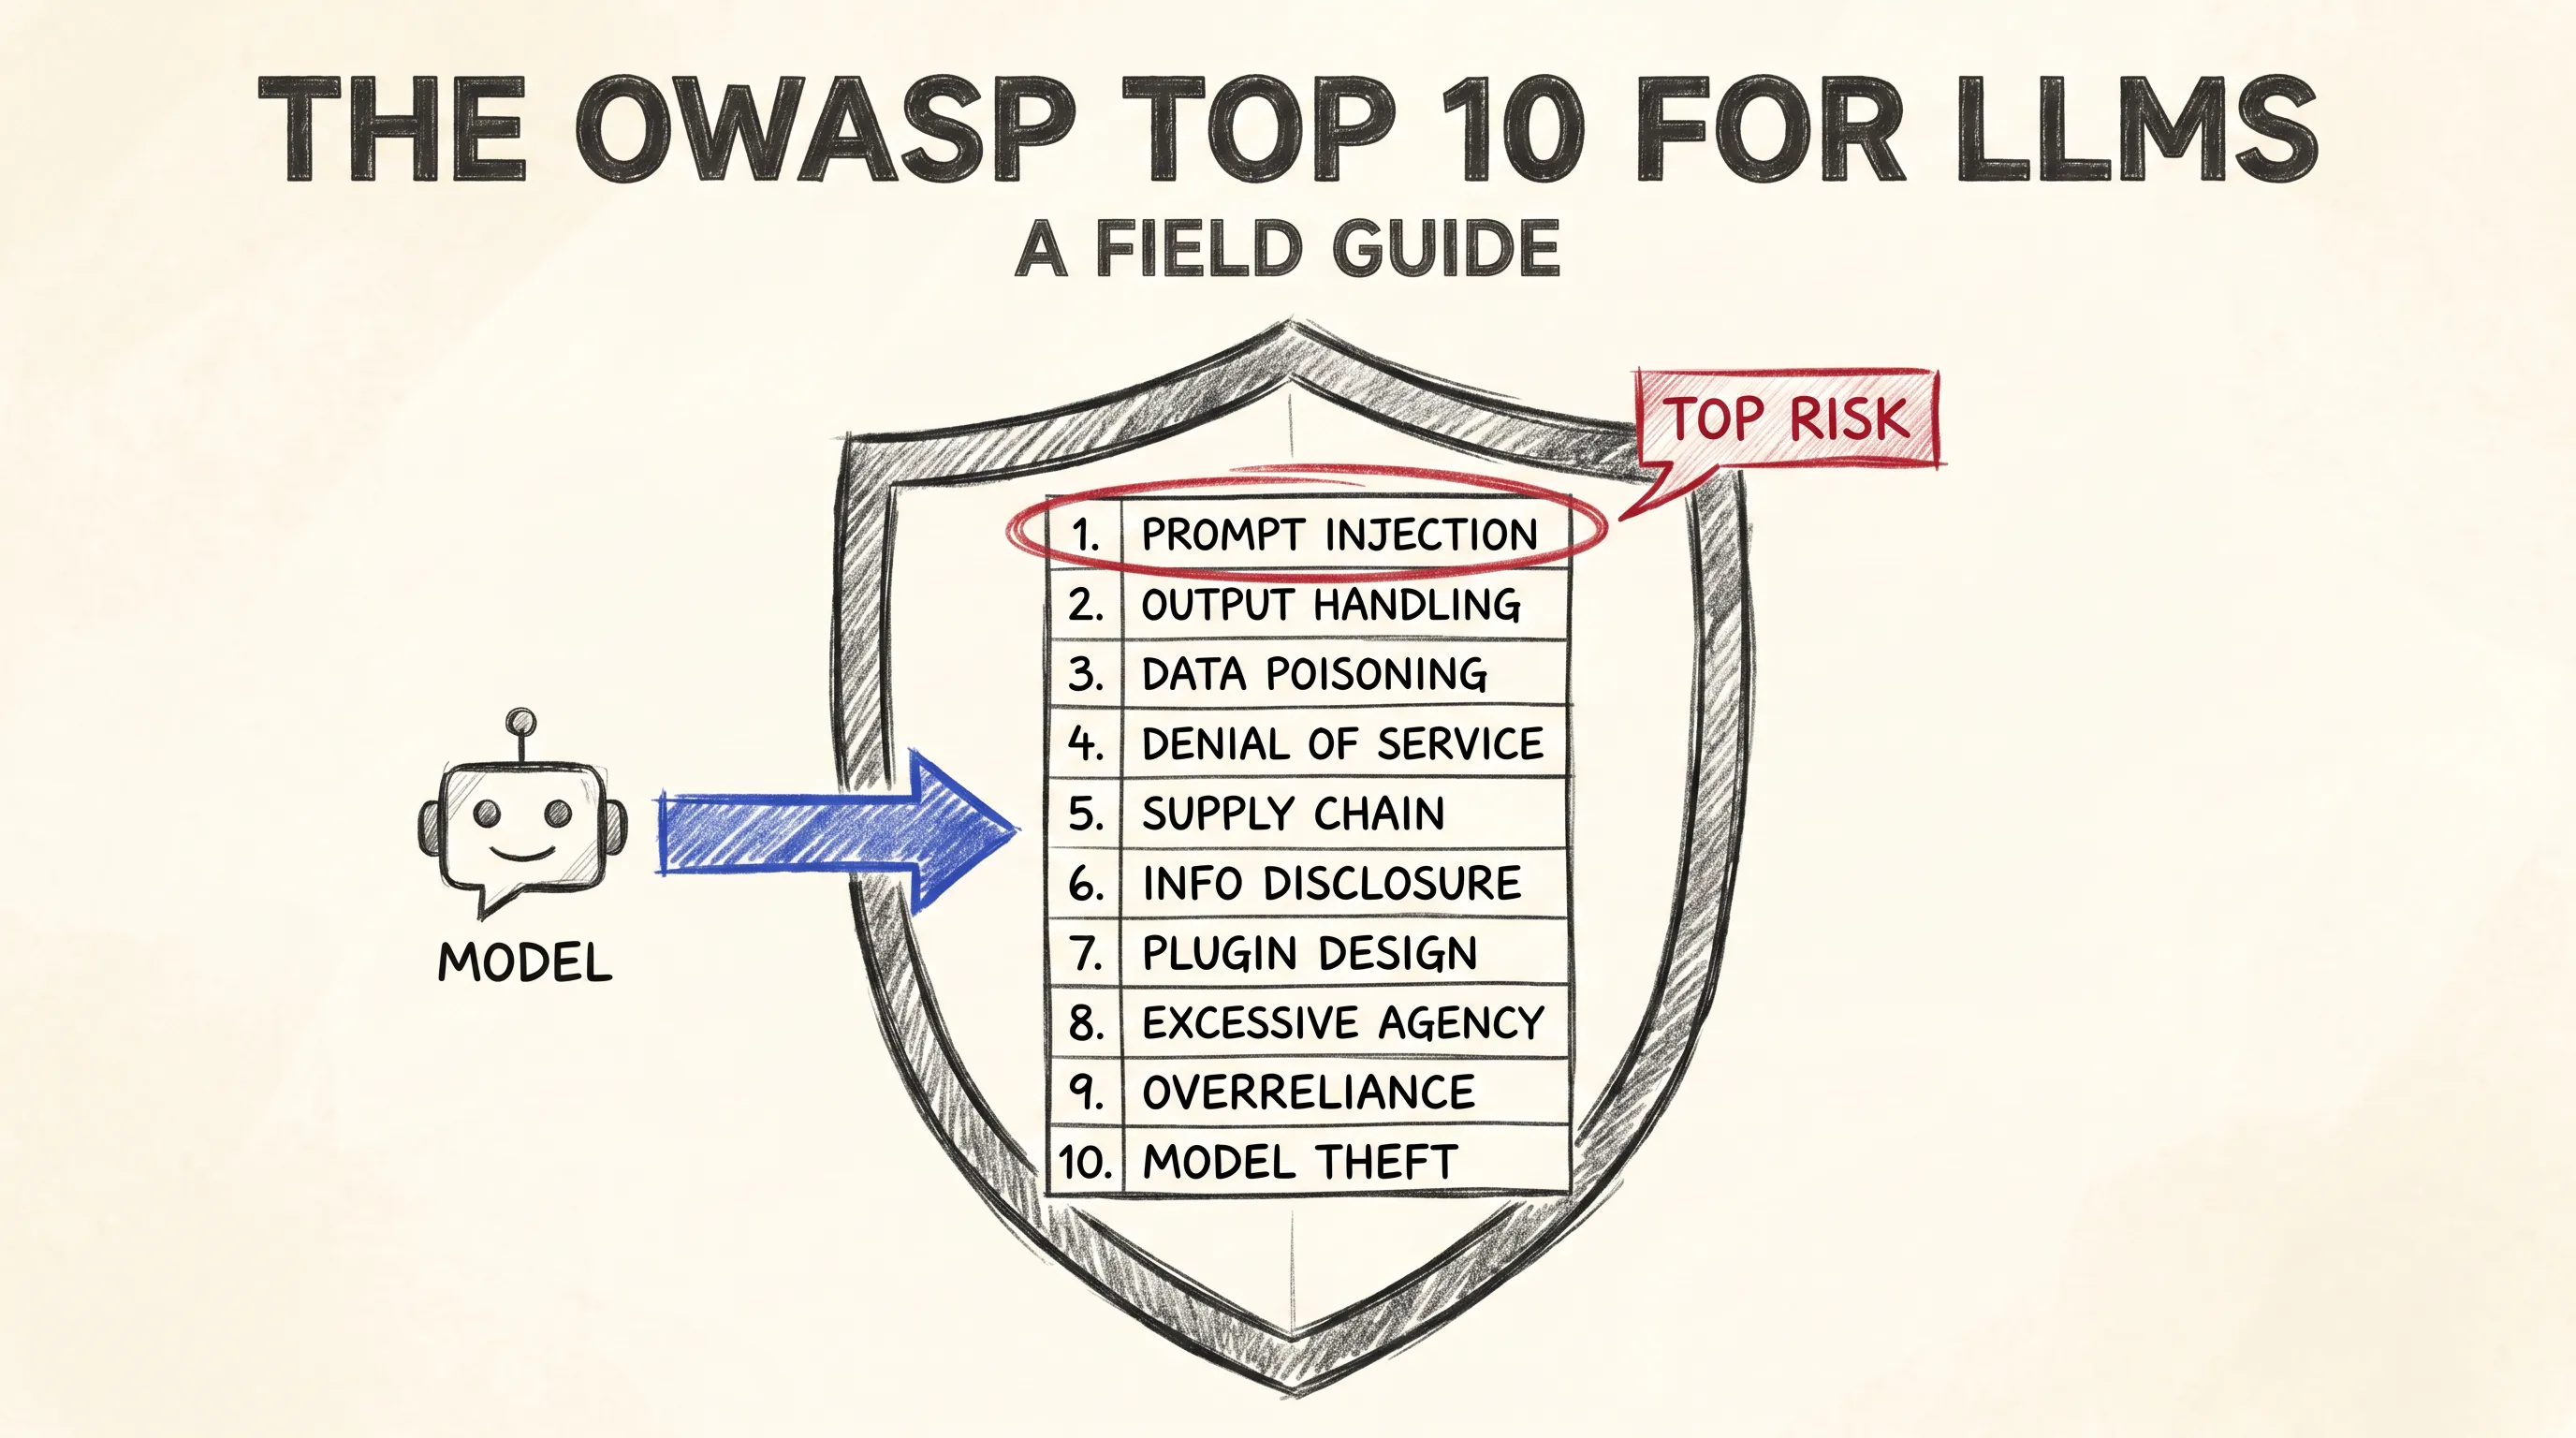 llm-security9 min read
The OWASP Top 10 for LLMs: A Field Guide
A field guide to the OWASP Top 10 for LLM Applications, the ten vulnerability categories that define modern AI application security.
-
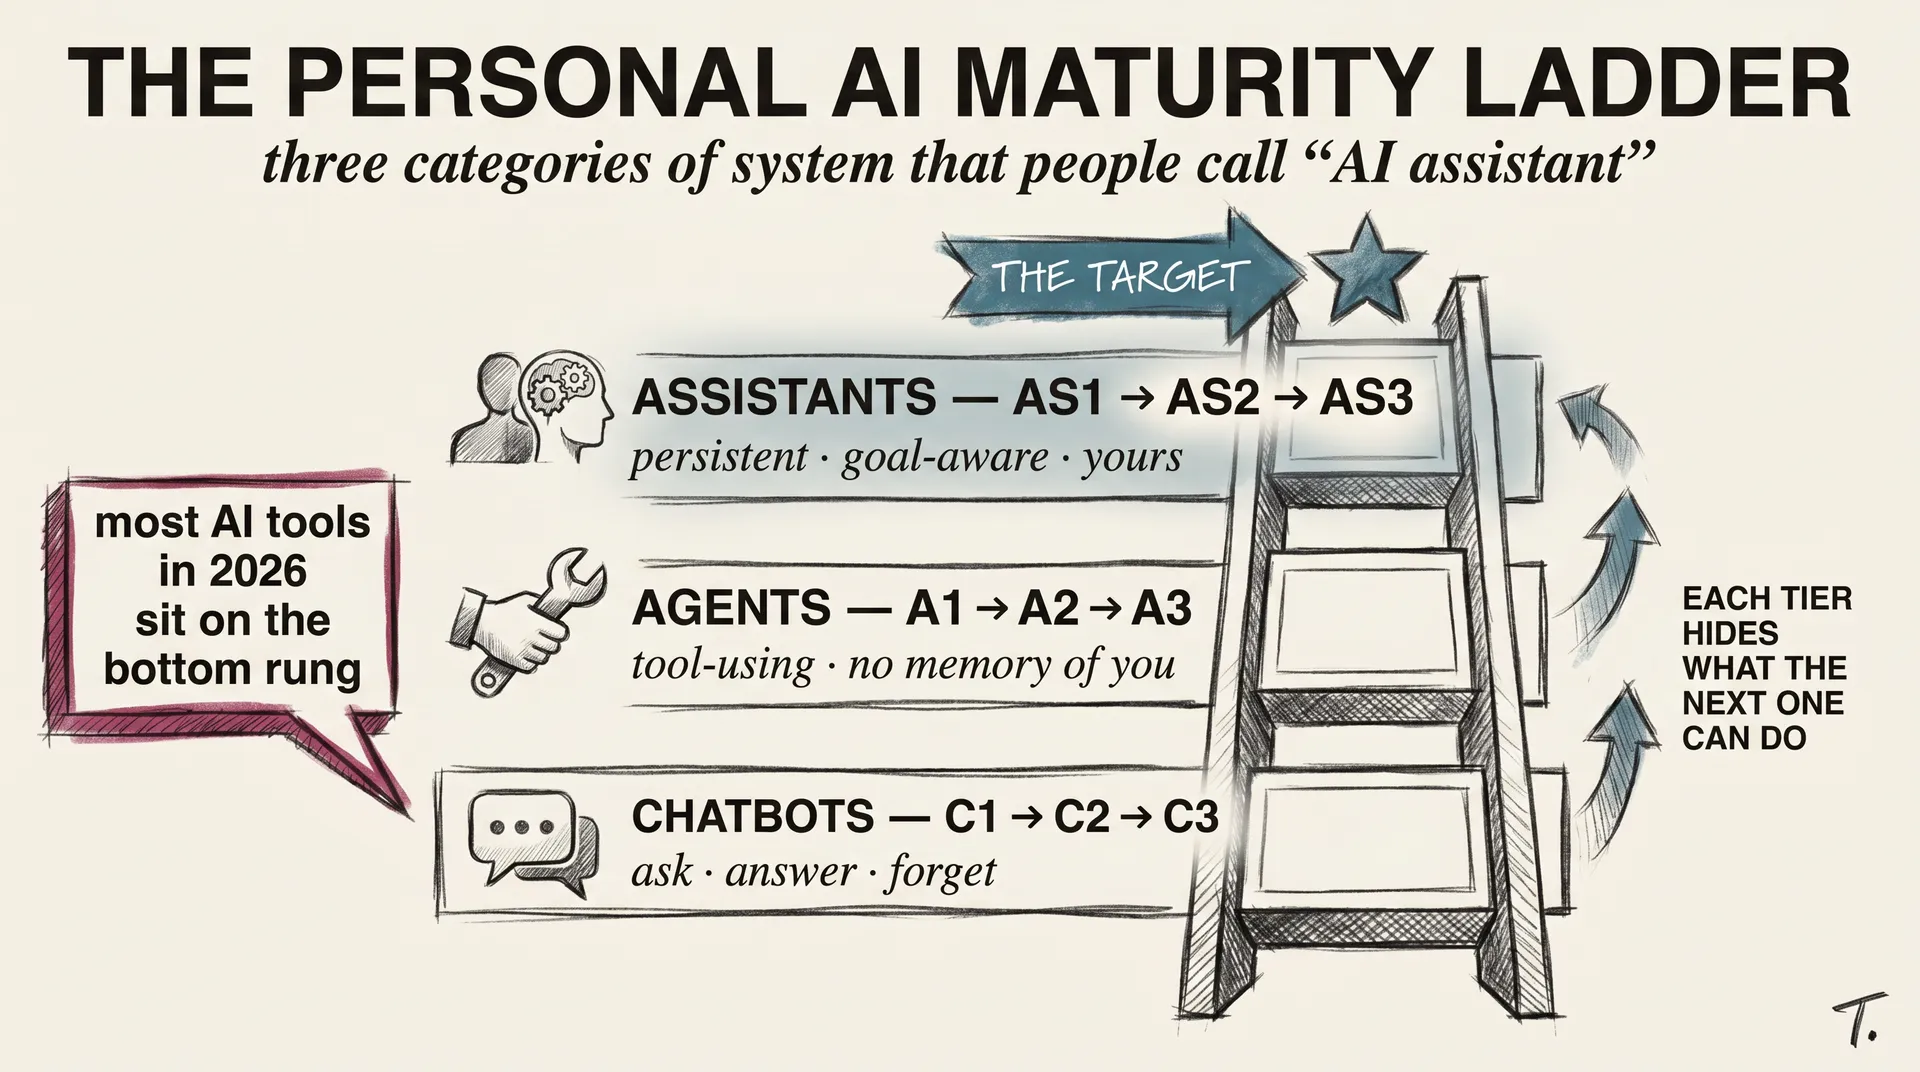 llm-concepts8 min read
Personal AI Infrastructure: The Climb From Chatbot to Assistant
Most AI tools today are chatbots in a costume. The real ladder has three tiers, and 2026 finally made the top one buildable at home.
-
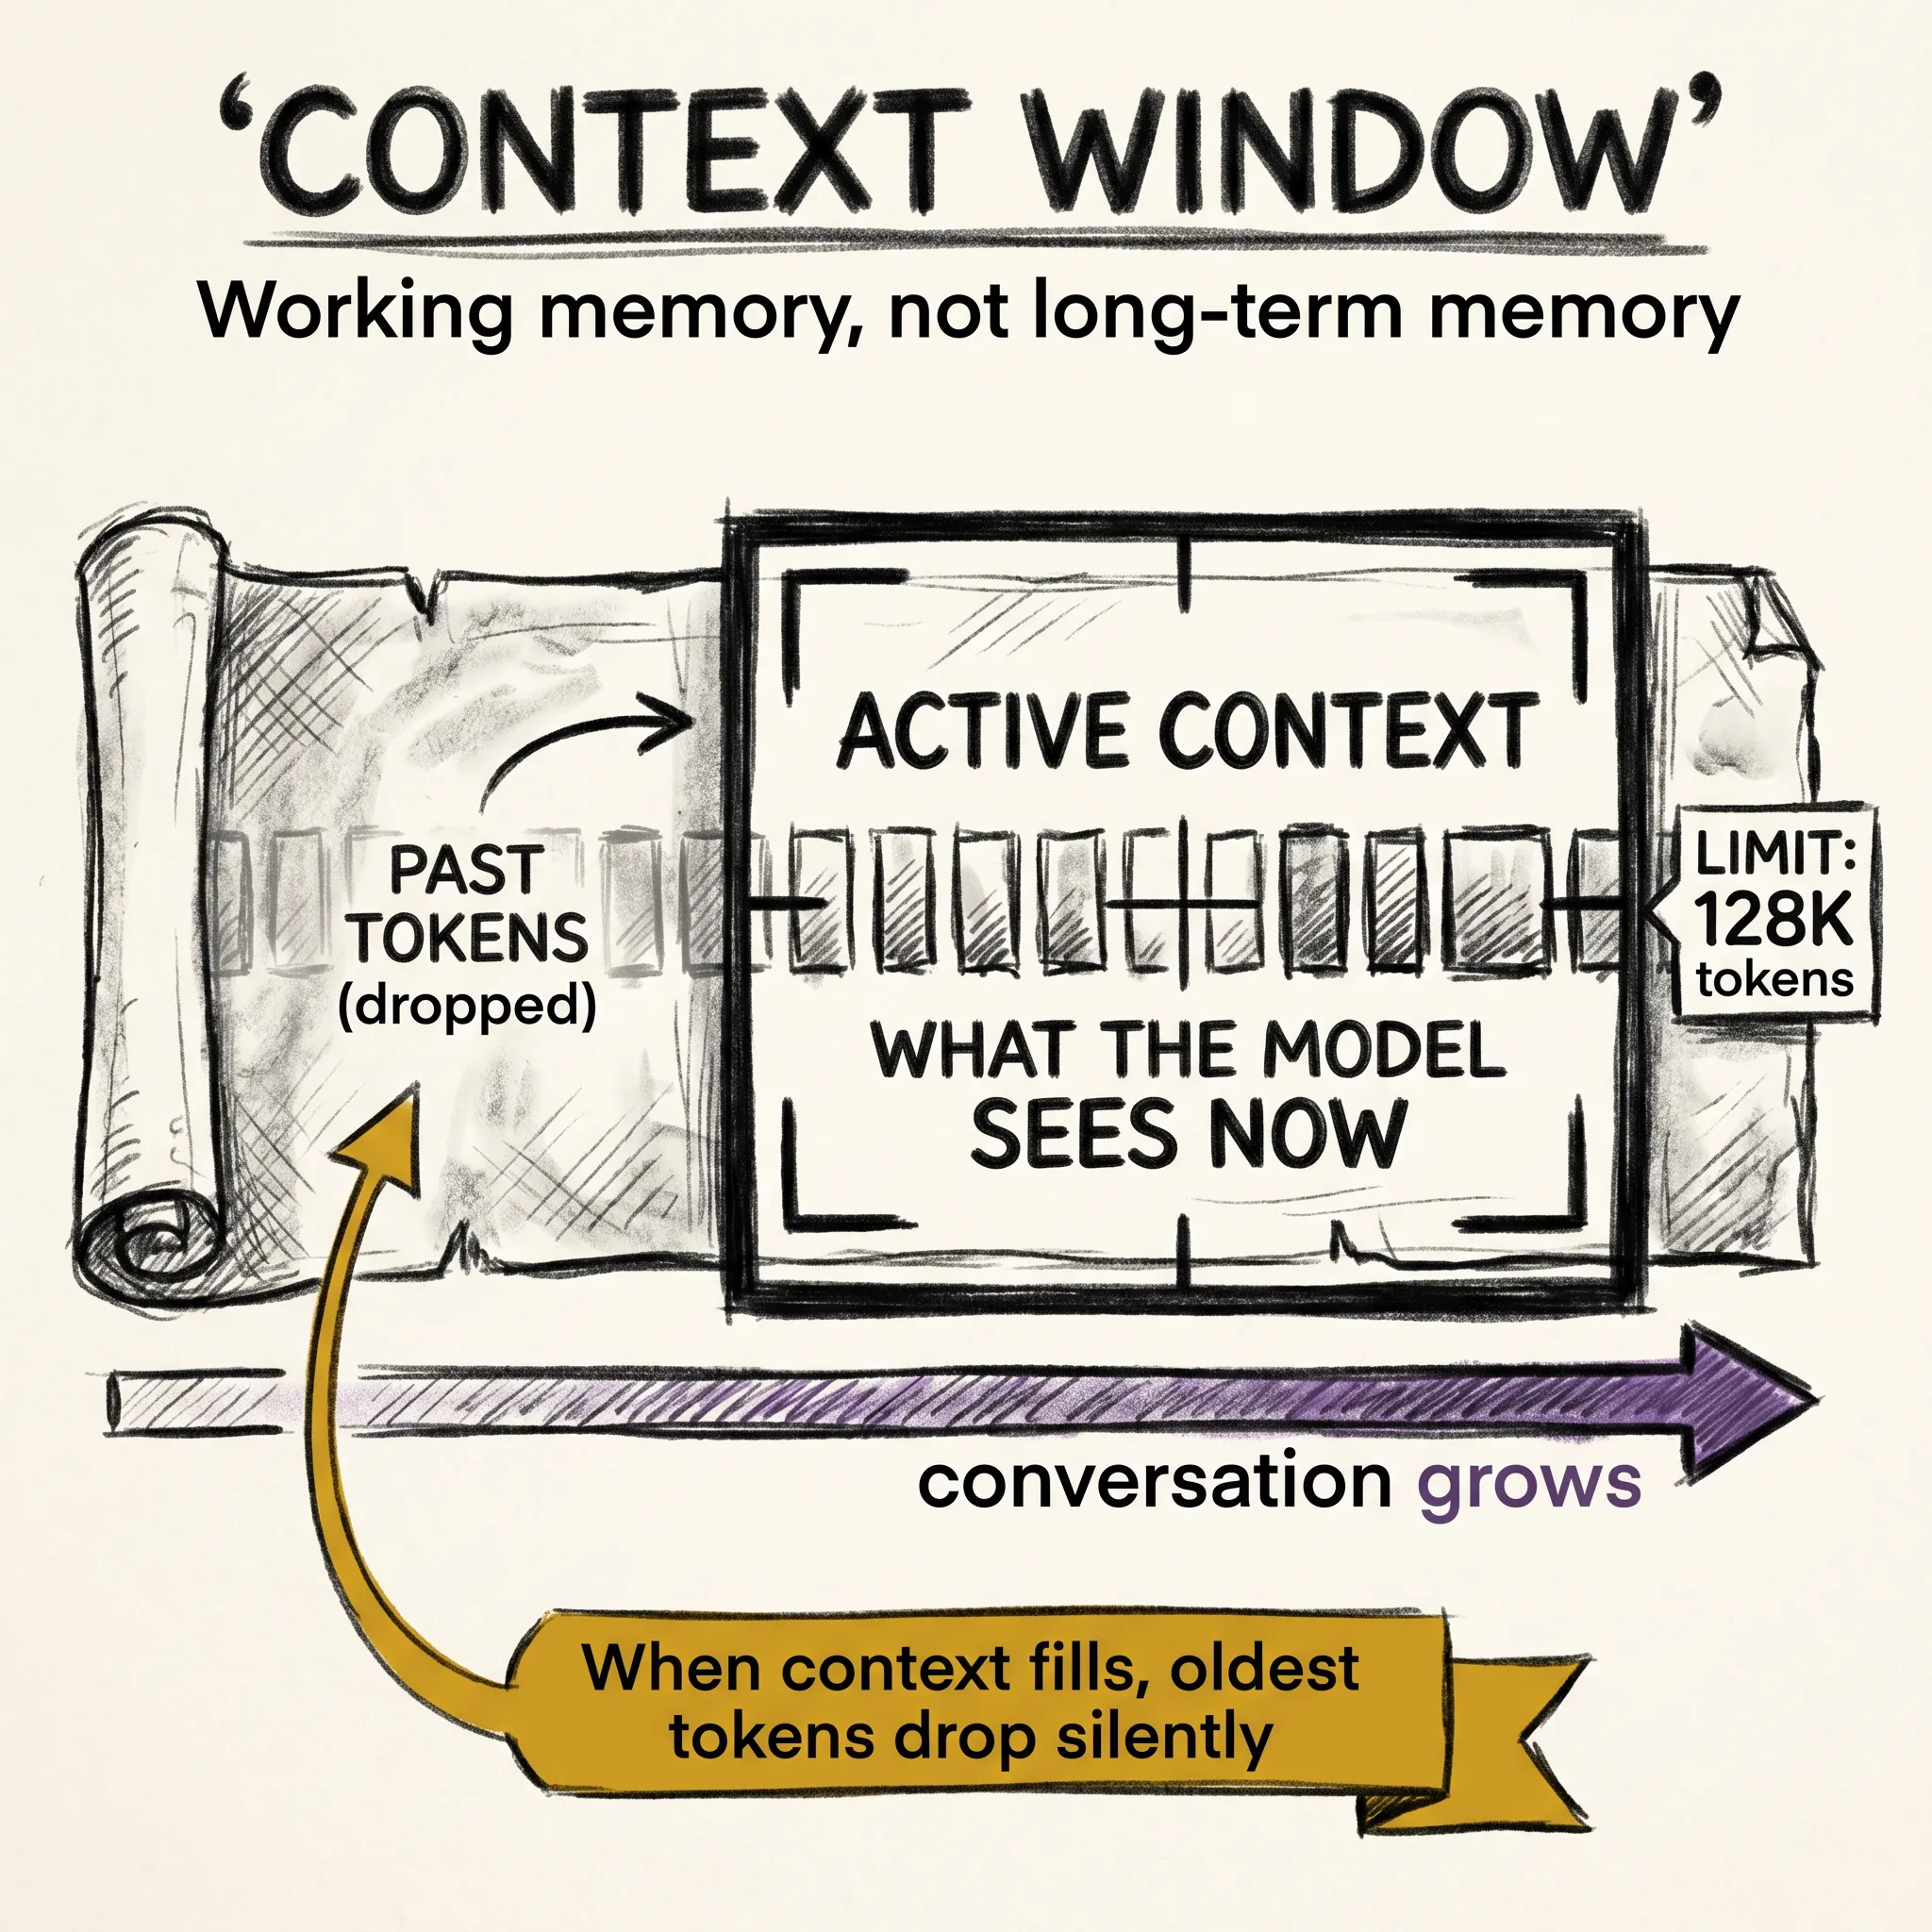 ai8 min read
Context Windows: Why Your AI Has a Working Memory Limit
Context windows are not memory. They are working memory. Here is what the model can see right now, why extending that limit is hard, and what it costs to try.
-
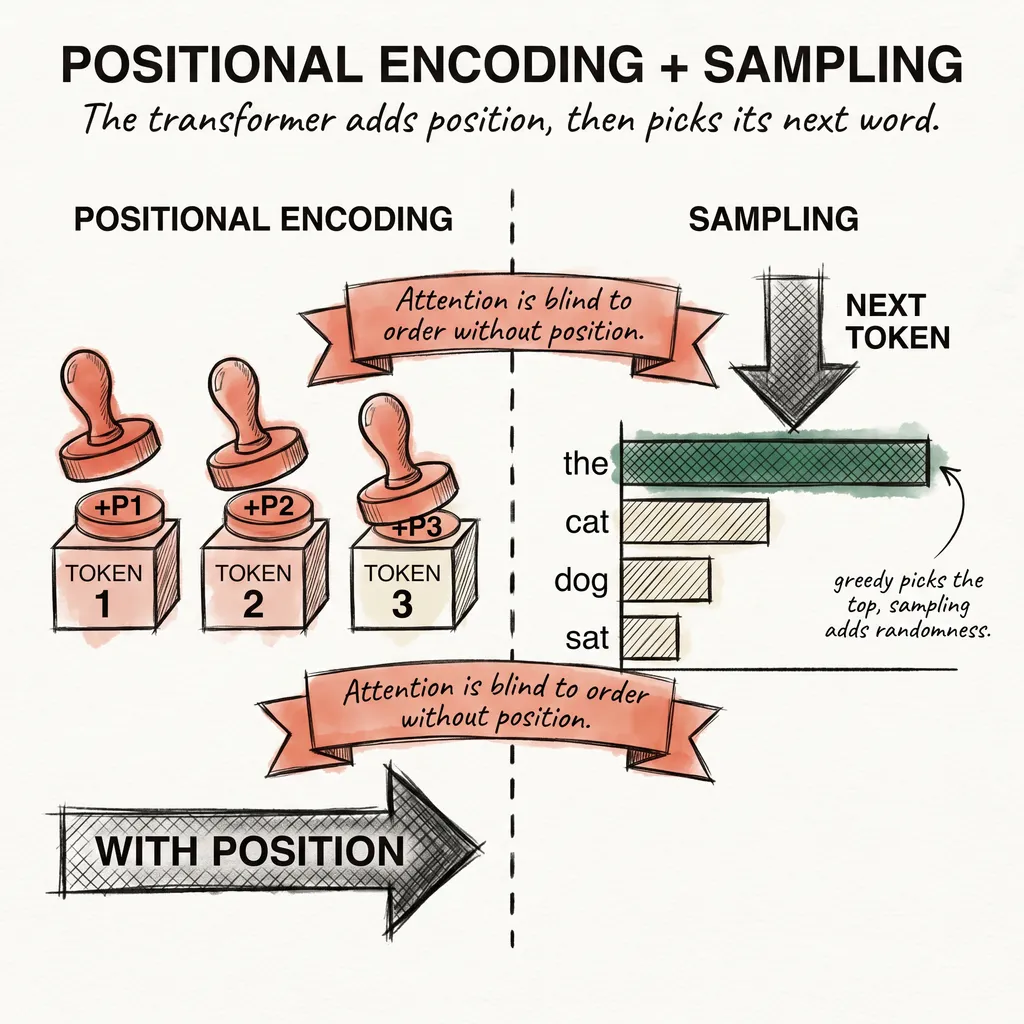 ai9 min read
Positional Encoding and Sampling: How the Transformer Finds Position and Picks Its Next Word
Attention cannot tell 'the dog bit the man' from 'the man bit the dog.' Positional encoding fixes that. Then sampling decides what word the model actually says.
-
 ai7 min read
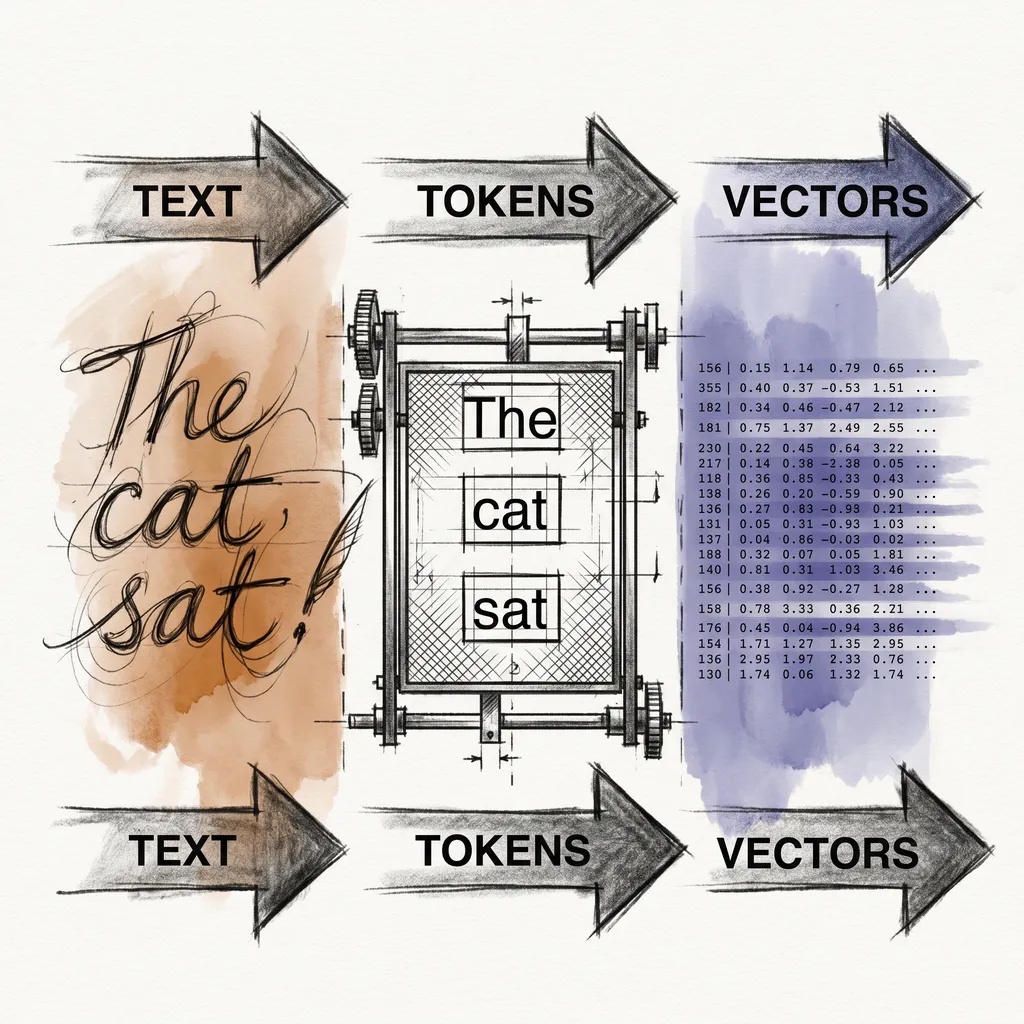
Tokens and Embeddings: How Raw Text Becomes Numbers the Model Can Use
Before the transformer can do anything, it must turn your prompt into numbers. Here is exactly how that works, from raw characters to dense vectors.